We Design, Develop and Manufacture our Products in Silicon Valley, USA.
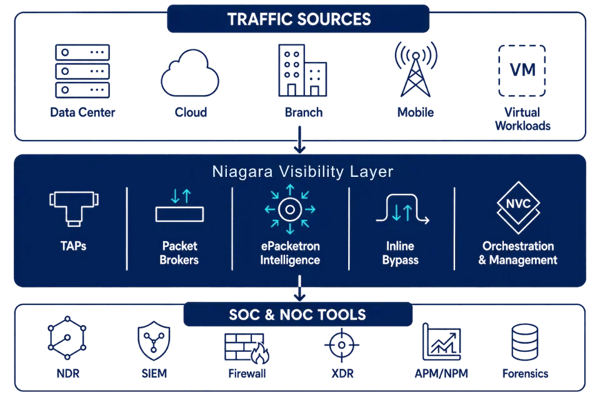
Niagara Networks™ delivers all the essential building blocks for high-performance visibility across physical and virtual network infrastructures. Our comprehensive portfolio includes Network Packet Brokers, Bypass Switches, Network TAPs, and a unified orchestration layer for seamless visibility and control.
Advanced Network Packet Brokers
Network Packet Broker Aggregators
Niagara Networks™ solutions enable NetOps and SecOps teams easily and efficiently operate and administer multiple security platforms and service scale, while reducing operational expenses and downtime.
Niagara Networks™ partners with world-class technology leaders to provide high performance network visibility and security.
Our partners include companies that are part of our technology alliance and companies who take part in distributing Niagara's solutions.
Expanding reach and value through a strong
worldwide network of channel partners
Empowering innovation through strategic
alliances with leading technology providers
Niagara Networks Visibility Gap Assessment offers your business both security and a real-time visual representation of your network infrastructure, showing exactly how packet broker optimization reduces tool overload. Optimize your network and view your visibility architecture visually mapped, from core switches to uplinks, SPAN sessions, TAP insertion points, packet brokers, and security tools.

How it Works?
1. Upload a sanitized Cisco switch configuration
2. Visualize full topology, SPAN sessions, TAP points, and tool feeds
3. Model optimization and receive a full report showing raw vs. optimized traffic
Niagara Networks changes network visibility from a bunch of monitoring feeds to a secure and managed traffic intelligence layer, capturing the right traffic, optimizing it for each of the tools, and protecting mission-critical systems and networks from blind spots and downtime.
Capture complete packet data from physical, virtual, cloud, and hybrid environments using TAPs, virtual TAPs, and bypass access points.
Use packet brokers and network intelligence to filter, deduplicate, slice, decrypt, replicate, and load-balance traffic before it reaches your tools.
Feed SOC, NOC, monitoring, and security platforms with reliable, policy-driven traffic while protecting uptime across mission-critical networks.
When you upload your sanitized Cisco switch config file (interfaces and span sessions only — no IPs, no routing tables). Within seconds, you’ll receive:
A mapped-out graphic of your network topology and all active span/mirror sessions
Auto-detection of span oversubscription and packet drop issues
Interactive TAP and packet broker deployment across your real links
Traffic optimization modeling - all in real time - Layer 4 filtering, deduplication, packet slicing, NetFlow generation
Full downloadable report with raw vs. optimized traffic per security tool
Everything runs entirely in memory, with nothing stored. Want full control? Run it on your own system via our Docker image.
Full downloadable report, showing raw vs. optimized traffic per security tool. Get an assessment report that summarizes monitored zones, deployed visibility links, raw traffic, optimized traffic, with extra recommended visibility architecture.
Vital network perimeters are identified and the primary traffic vectors designated for security extraction and security monitoring.
Every piece of raw traffic is ingested from the network prior to optimization filters being applied.
Once the visibility gap assessment is complete, Niagara Networks helps to design the visibility layer using TAPs, packet brokers, bypass, ePacketron intelligence, virtual visibility & orchestration. Our visibility portfolio helps SOC and NOC teams move from fragmented monitoring feeds to a managed visibility layer that enhances overall performance and security.
Niagara Networks Appliance Comparison Matrix
Get encrypted traffic visibility restored with SSL/TLS decryption and offload advanced packet processing, including application filtering, packet slicing, deduplication, NetFlow/IPFIX, data masking, and traffic optimization across diverse enterprise use cases. Read more
Currently, our tool offers support for Cisco IOS and Cisco Nexus configurations.
Network Visibility’s assessment models how traffic optimization techniques can reduce the amount of raw traffic being sent to monitoring and security devices. This can include Layer 4 filtering, deduplication, packet slicing, unsampled NetFlow/IPFIX exportation, and load balancing onto NDR, SIEM, IDS, IPS, APM, NPM, and other tools.
This is how much raw traffic enters the visibility layer and how much it can be decreased prior to delivery to each tool. The packet slicing technique can help to decrease the traffic volume before sending it to performance monitoring tools, while the deduplication technique can eliminate duplicate packets that can overload NDR or analytics platforms.
It is better because a generic ROI calculator only makes assumptions, while the Niagara Networks Visibility Assessment Tool is based on your actual network configuration, providing a more practical and environment-specific view of your visibility gaps and optimization potential.
© 2026 Niagara Networks. All Rights Reserved.