close
close-x

Site Search

    4540 - High-density 100Gb Packet Broker Solution

    ACCELERATE THE NETWORK INTELLIGENCE LAYER

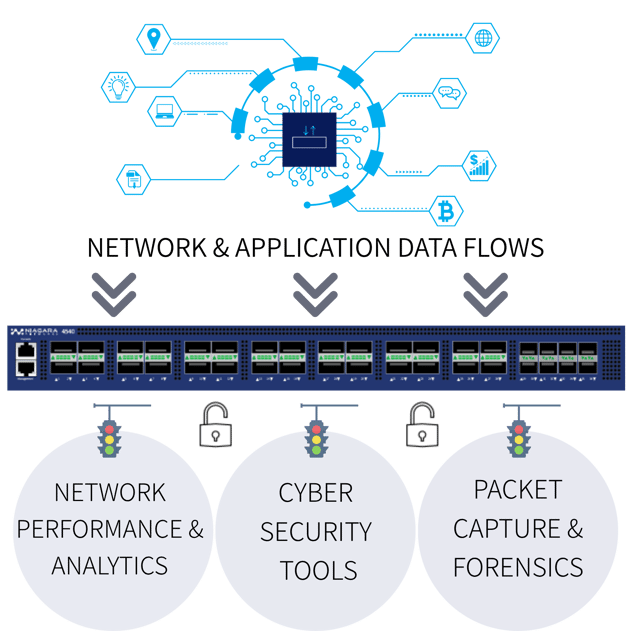
    Enhance visibility and control through high-performance aggregation, filtering, replication, load balancing, and traffic grooming across 10/25/100G interfaces - all powered by a 3.2 Tbps non-blocking architecture that ensures lossless, line-rate delivery of traffic to the right tools.
    Intelligent
    • Provides advanced aggregation, replication & multi-level filtering
    • Ensures precise & reliable traffic distribution across tools
    • Simplifies complex network architectures
    • Enables seamless traffic flow for performance & security monitoring
    • Enhances the efficiency and accuracy of NOC & SOC tools


    Scalable Visibility
    • Flow-aware policy enforcement: packet slicing, de-duplication, tunnel awareness
    • Optimize tool utilization & reduce data overhead in hybrid, mixed-speed environments
    • Simplify APM/NPM analytics & reporting
    • Enhance security analytics with efficient, advanced threat inspection
    • Boost tool performance & scalability by minimizing redundant data
    Adaptive
    • High-density, pay-as-you-grow architecture with flexible port options
    • Optional Packetron acceleration extends visibility with deep packet inspection, TLS decryption & Layer 7 analytics
    Packetron - Adding Advanced Network Intelligence up to Layer 7

    ADDING THE ePACKETRON INTELLIGENCE ARCHITECTURE TO THE 4540

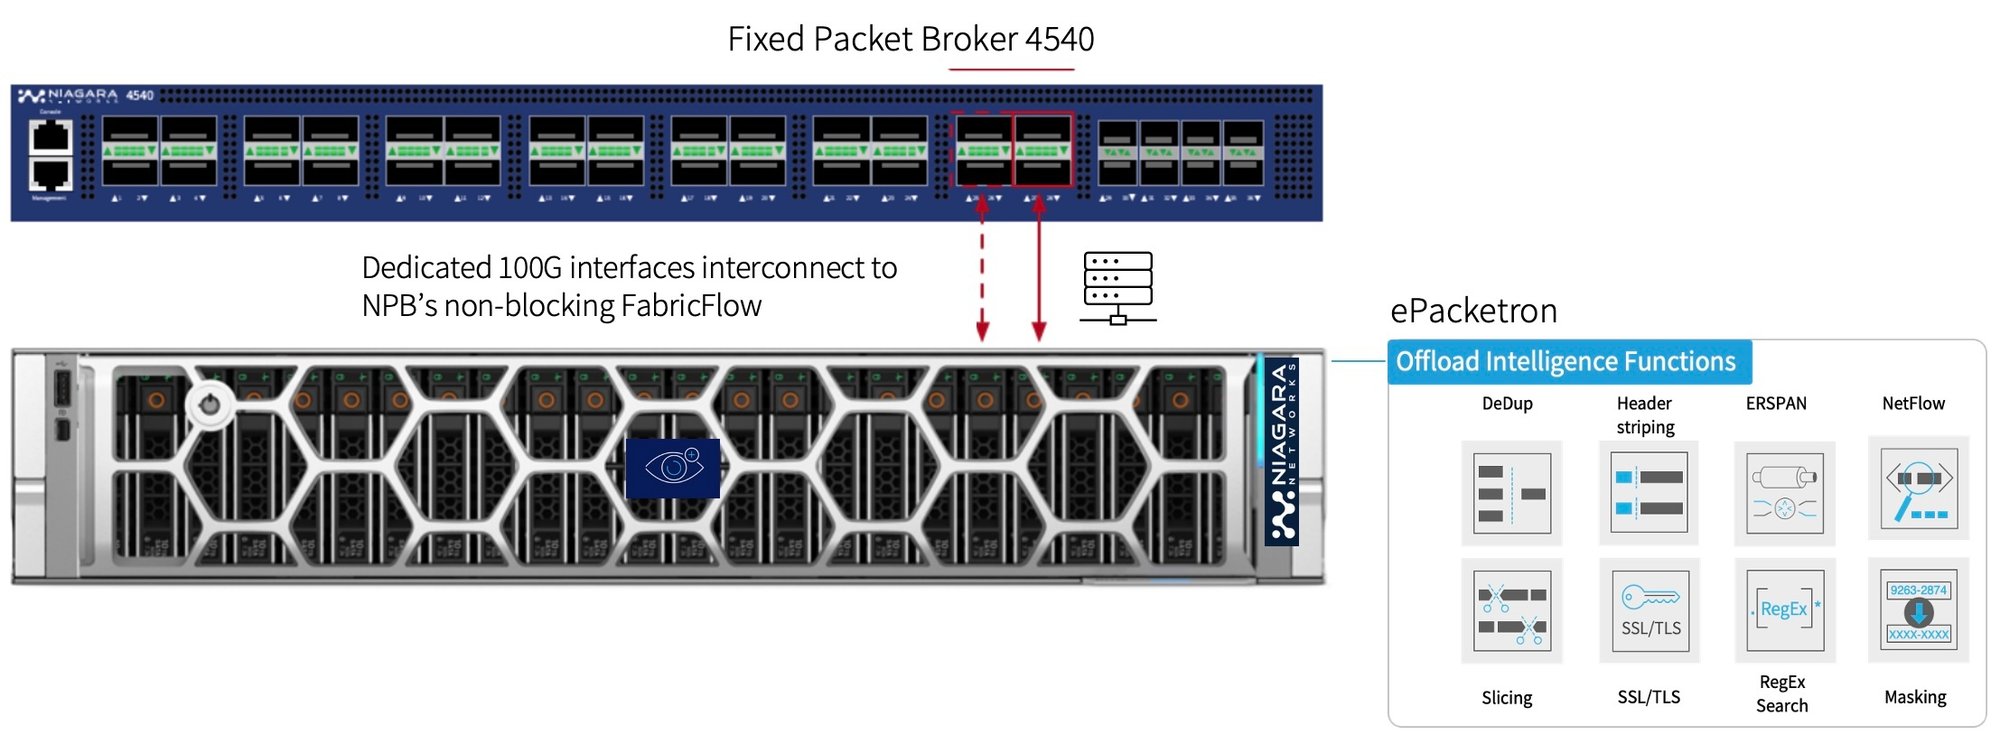
    The Niagara 4540 Next-Generation Network  Packet Broker (NGNPB) supports modular acceleration through up to two Packetron line-card modules, enabling advanced packet processing directly within the visibility fabric. Each module connects to the 3.2 Tbps non-blocking FabricFlow™ architecture via dedicated 100G interfaces, allowing any ingress or egress port to benefit from enhanced Layer 2–7 packet intelligence.
    The architecture is future-ready, supporting seamless migration to next-generation ePacketron appliances for greater processing power, application awareness, and multi-tenant performance.

    Offload and Accelerate

    Offload intensive packet processing tasks, such as deduplication, slicing, and SSL/TLS decryption, from monitoring & security tools to the visibility layer.
    This improves throughput efficiency, tool performance, and resource utilization across the monitoring infrastructure.

    Scale as Capacity Grows

    Deploy one or two Packetron modules based on processing requirements, with a clear upgrade path to ePacketron acceleration for extended compute capacity and advanced feature sets.
    The modular design enables pay-as-you-grow scalability as network traffic and analysis demands evolve.

    Gain Deep Insight

    Leverage packet and flow-level visibility up to Layer 7 for advanced analytics, compliance monitoring, and forensic visibility.
    Integration with FabricFlow provides precise flow control, dynamic traffic optimization, and consistent performance under heavy load.

    From raw network & application data flows to actionable insights

    Next-Generation Packet Broker For High-Demand Networks 

    The 4540 operates as a true Next Generation Network Packet Broker (NGNPB), supporting advanced packet broker functions such as de-duplication, packet/flow slicing, application-aware filtering, tunnel termination, NetFlow generation & Packetron-accelerated L4–L7 processing.


    Terabit Visibility Fabric

    • Up to 28 × 40/100Gb and 8 × 1/10/25Gb ports
    • 3.2Tbps non-blocking switching fabric
    • Full any-to-any port connectivity at line rate
    • Supports up to 2 pluggable Packetron modules 
    • 1RU Compact Form Factor 

    Scalable & Reliable

    • Stackable via any port for expanded visibility fabrics
    • Compact design with dual hot-swappable power supplies & fans
    • Integrates with external inline bypass for continuous, always-on availability

    Intelligent Traffic Control

    • FabricFlow aggregation, replication & filtering (L2–4, UDB)
    • Advanced tunnel handling for ERSPAN, VXLAN, MPLS, GRE, NVGRE, GENEVE and  mobile GTP
    • Flexible load balancing: L2–L4 hashing, utilization-based, or session-sticky modes

    Deep Packet Intelligence

    • Packetron acceleration modules for hosting third-party virtual applications and advanced packet intelligence functions up to Layer 7
    • Supports application filtering, de-duplication, packet slicing, header stripping, TLS decryption, data masking, NetFlow/IPFIX generation, REGEX and 3G/4G/5G NSA mobile visibility

    Scalable Performance

    • Single-bay packet acceleration module design
    • Supports up to 2 rear Packetron modules (up to 200G processing)
    • Future-ready for external ePacketron expansion


    De-coupled Software Architecture

    • Modular design based on microservices architecture enables independent software updates for Packetron & associated services.
    • Agile upgrade model for rapid deployment of new network intelligence features

    Open Visibility Platform

    • Supports 'open garden' application architecture
    • Enables third-party partner integrations for analytics, security & network intelligence applications Learn more

    Expandable Network Intelligence for Future Growth

    • Pay-as-you-grow architecture supporting multiple processing profiles
    • Built for high-speed Packet Acceleration and hybrid deployments  Learn more

    MADE in the USA

    Niagara Networks is among the few companies designing and manufacturing network visibility solutions in the USA, ensuring quality, reliability & security compliance Learn more
    4540 - Advanced Packet Broker Use cases

    Use Cases

    Aggregate, filter, and distribute traffic intelligently across multiple monitoring, performance, and security tools.
    Ensure efficient utilization of existing infrastructure by sending only relevant traffic to each tool.

    Niagara Networks Packet Brokers, combined with the Open Visibility Platform, collect, aggregate, and filter traffic across physical and virtual environments to deliver only relevant, optimized data to SIEM and analytics tools.
    This integration enables session-aware load balancing, removes duplicate packets, and supports centralized or distributed NFV-based inspection, providing agile, scalable visibility for SecOps and NetOps operations.
    Implement packet slicing to reduce tool load and expose only necessary traffic, while simultaneously exporting NetFlow v9 metadata to multiple collectors - enabling both deep security inspection and distributed traffic analytics from a single visibility node.
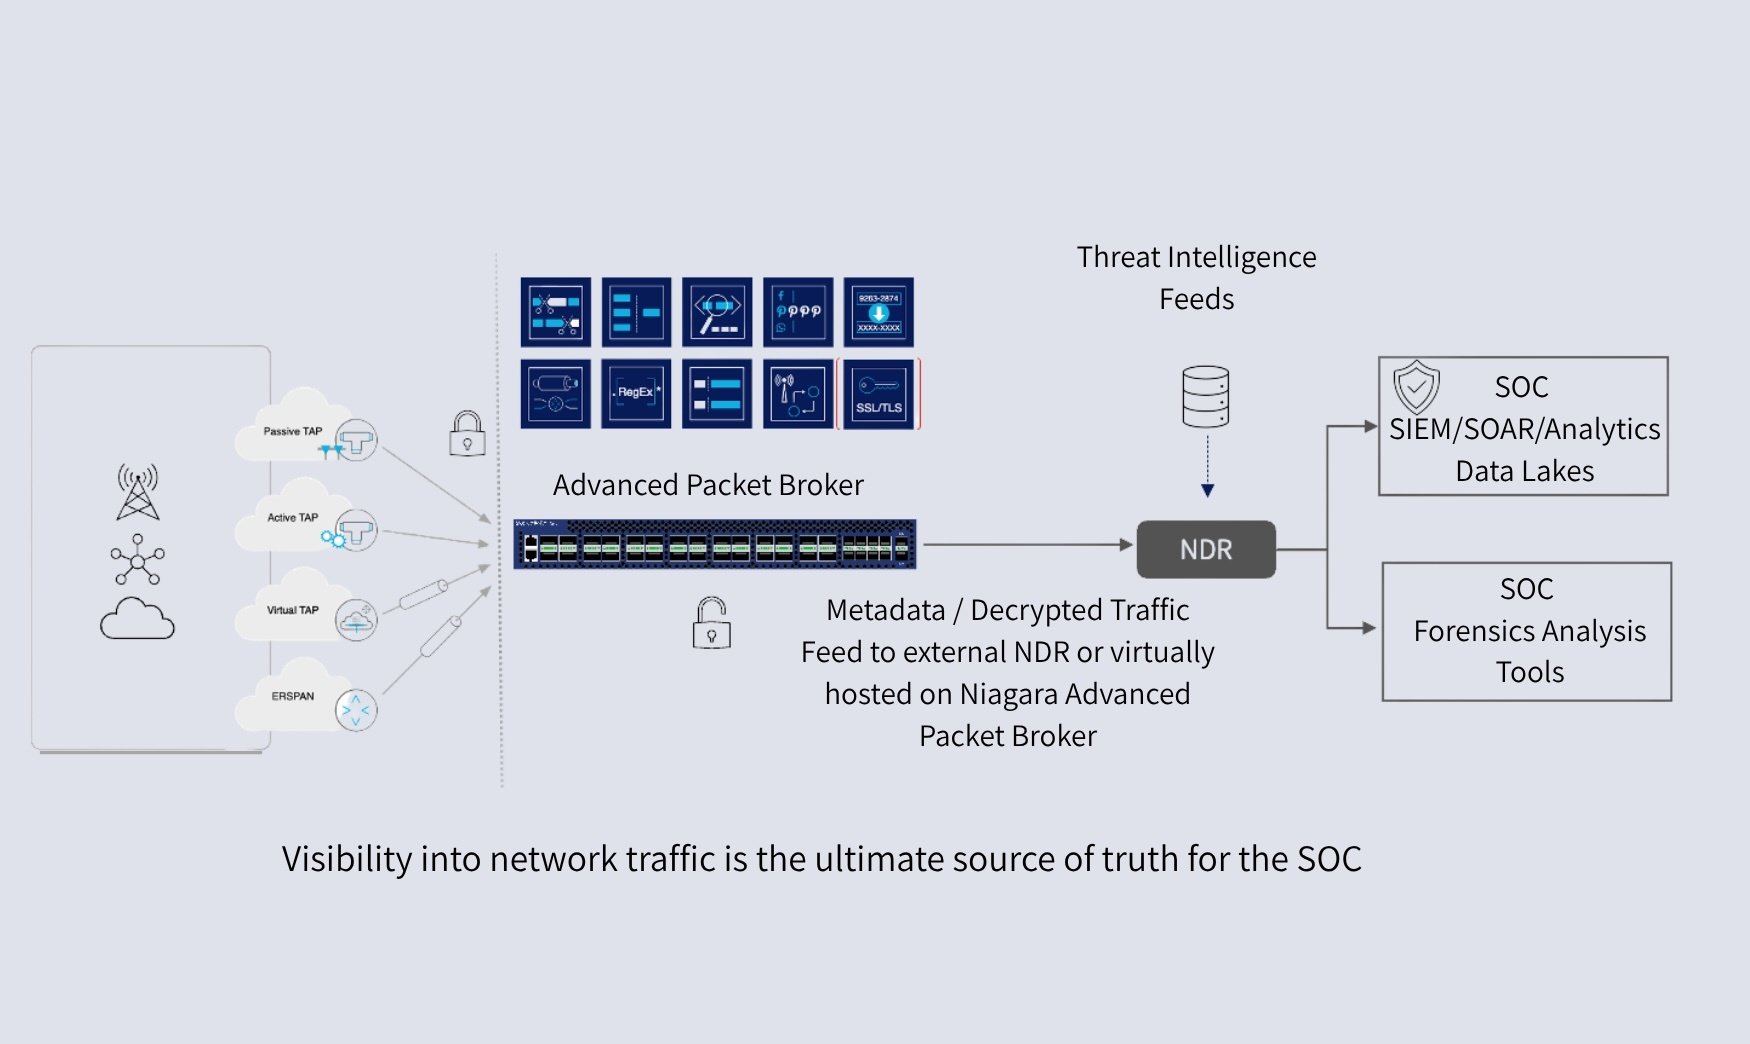
    Advanced Packet Brokers extract and filter encrypted sessions or metadata (e.g. JA3, SNI, TLS attributes) and feed them to NDR platforms for behavioral analysis - detecting threats without full decryption while minimizing exposure, reducing tool load, and preserving compliance.
    A three-stage architecture combining strategic traffic interception (TAPs/packet brokers), flow-metadata generation and high-speed anomaly detection, enabling service-providers and national backbone operators to detect and mitigate multi-vector DDoS attacks (including Tbps-scale) rapidly & automatically.
    Duplicate packets from port-mirroring and multi-tap setups flood monitoring tools, driving up storage demands, false positives and processing overhead. By leveraging flow-aware deduplication in the visibility layer, organizations can offload duplicate removal before data hits security tools - improving SOC/NoC accuracy, reducing resource usage & enabling high-throughput monitoring at scale.

    "We needed an absolutely perfect packet collection system - not just fault-tolerant, but fault-free - and Niagara solution provided that."

    - Data Analysts -


    Continuous monitoring is a core requirement of the NIST Cybersecurity Framework 2.0, ensuring that adverse events are detected early and acted upon before they escalate. Traditional methods such as SPAN ports or mirroring are no longer sufficient for today’s high-bandwidth and hybrid environments, where blind spots and encrypted traffic can mask threats.
    Niagara Networks addresses this challenge by delivering complete, real-time visibility across physical, virtual, and cloud infrastructures.
    With advanced capabilities such as inline bypass, TLS decryption, packet slicing, and traffic aggregation, Niagara enables NetOps and SecOps teams to continuously monitor all traffic flows, detect anomalies, and ensure compliance. This visibility directly supports
    the Detect (DE.CM) category of NIST CSF 2.0, helping organizations monitor networks, external services, and computing resources
    without compromise.

    4540 Packet Broker – Frequently Asked Questions (FAQ)

    The 4540 is a high-performance, 3.2 Tbps non-blocking packet broker designed for 10/25/100G visibility environments. It aggregates, filters, and distributes network traffic to monitoring and security tools, ensuring line-rate, lossless performance for SOC and NOC operations.

    Unlike traditional packet brokers limited to Layer 2–4 visibility, the 4540 supports Layer 7 intelligence through Packetron acceleration. It also integrates with Niagara’s Open Visibility Platform (OVP), enabling 3rd-party applications and virtualized analytics directly on the same platform.

    A Next Generation Network Packet Broker (NGNPB), often called an Advanced Packet Broker, is a modern visibility platform that goes beyond basic traffic aggregation. It performs intelligent processing such as de-duplication, packet/flow slicing, tunnel termination, application-aware filtering, NetFlow export, and L4–L7 visibility functions to optimize traffic delivery to security and monitoring tools.

    The 4540 features a modular, pay-as-you-grow design that supports up to 3.2 Tbps of non-blocking throughput. It can host one or two Packetron acceleration modules today, with a clear upgrade path to future ePacketron (external) options for expanded processing power.

    With Packetron or ePacketron* acceleration, the 4540 enables advanced functions such as deduplication, packet slicing, TLS/SSL decryption, header stripping, RegEx filtering, data masking, mobile GTP correlation, and NetFlow/IPFIX generation enhancing visibility and reducing tool load.

    Yes. The 4540 supports inline, out-of-band, and hybrid configurations. It can operate as a packet broker, active TAP, or combined solution, ensuring maximum flexibility for visibility and security architectures.

    The platform integrates seamlessly with the Niagara Visibility Controller (NVC), providing centralized management, policy automation, and FabricFlow™ orchestration across multiple visibility nodes. In addition, standard automation is supported via REST API for third-party integration and management.

    Common deployments include tool optimization and load balancing, encrypted traffic visibility, flow-level analytics and forensics, and SIEM data optimization.
    As a physical 100G appliance, the 4540 is typically deployed on-premises or in private data centers, but it can also be coherently configured and synchronized with virtual and cloud-based visibility tools through tunneled traffic connections.
    This enables complete hybrid cloud visibility for large enterprises and communication service provider networks.

    TLS decryption and other advanced Network Intelligence functions are enabled through the Packetron acceleration module.
    When TLS decryption is required, a Packetron module should be ordered and installed in one of the two rear hosting trays on the 4540.
    Each module connects directly to the non-blocking 3.2 Tbps switching fabric, enabling inline or out-of-band traffic decryption, application filtering, and other advanced functions such as de-duplication, packet slicing, and data masking.
    The system supports up to two Packetron modules, providing scalable performance and redundancy for demanding visibility environments.

    Unlock smarter visibility 

    Discover how Niagara’s Network Intelligence platform empowers NOC and SOC teams with advanced packet processing, deep traffic insight, and scalable performance across any environment.


    Fill out the form and our team will connect with you to explore how our solution can strengthen your network visibility strategy.


    Designed, Engineered & Manufactured in the USA

    From design to production, our solutions are built to the highest standards of quality, security, and performance, trusted by organizations worldwide and deployed in some of the world’s largest mission-critical networks.

    Connect with a Visibility Expert