close
close-x

Site Search

    4204  (1)

    Purpose-Built for Edge and Industrial Deployments

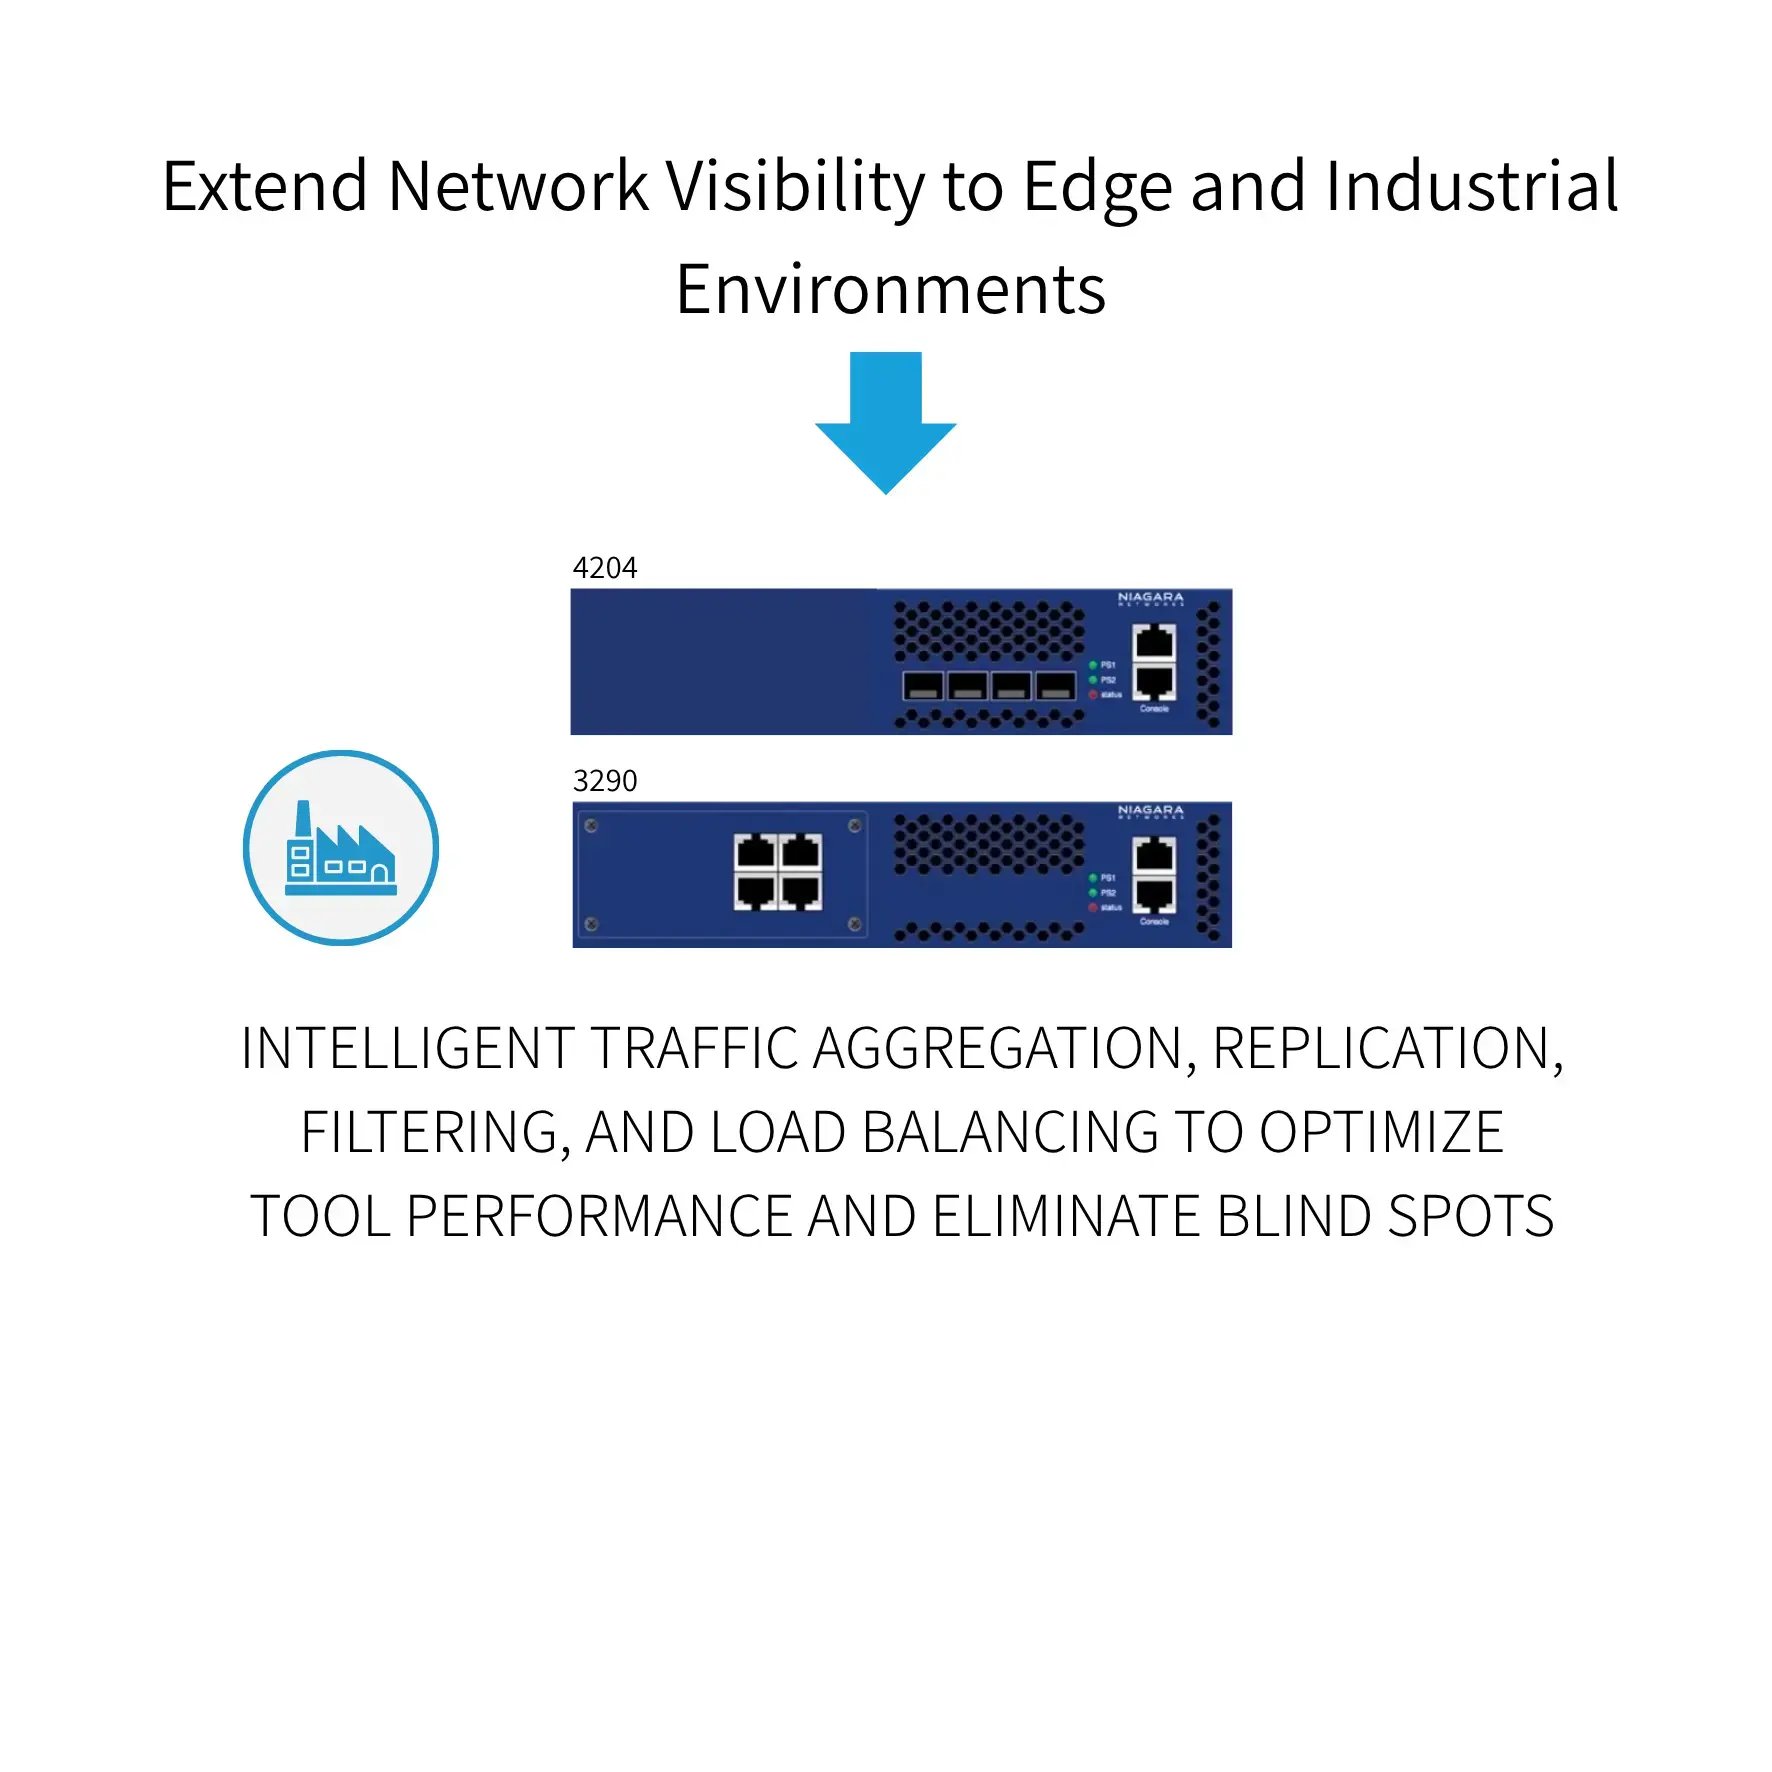
    The 4204 model addresses compact enterprise and edge use cases requiring flexible high-speed connectivity, while the 3290 model is optimized for industrial environments where reliability under harsh conditions is critical.
    The 3290 industrial packet broker ensures dependable operation in environments such as power substations, mining sites, and remote facilities, where temperature, vibration, and environmental constraints demand hardened infrastructure.
    Intelligent
    • Advanced traffic aggregation, replication, and multi-level filtering
    • Precise traffic steering to monitoring and security tools
    • Simplifies complex network visibility architectures
    • Enables efficient traffic delivery for performance and security monitoring
    • Improves the accuracy and efficiency of SOC and NOC tools

    Scalable
    • Flexible 1G copper and 1/10G fiber ports architecture for edge & industrial sites 
    • FabricFlow™ technology for intelligent traffic mapping and load balancing
    • Supports efficient traffic distribution across monitoring tools
    • Reduces tool overload and improves analytics efficiency
    • Ensures consistent performance in enterprise edge and industrial environments
    Adaptive
    • Compact half-width rack unit design for efficient rack space utilization
    • Edge aggregation of TAP and SPAN traffic sources
    • Flexible filtering and load-balancing policies
    • Simplifies deployment of monitoring and security infrastructures
    • Enhances operational efficiency across edge & industrial networks

    TURN NETWORK TRAFFIC INTO ACTIONABLE VISIBILITY

    The 4204 and 3290 models inherit Niagara Networks’ core packet broker capabilities, ensuring consistent visibility across all deployment sizes


    Non-blocking Visibility Fabric

    • Non-blocking switching fabric for deterministic traffic delivery
    • Compact half-width rack unit optimized for space, power, and cooling efficiency
    • 4204: 4 ports supporting 1G/10Gb
    • 3290: 4 ports supporting 1Gb copper - industrial deployments
    • Maintains fixed feature consistency across all NPB product tiers

    FabricFlow™ Traffic Intelligence

    • Advanced traffic mapping and policy-driven flow steering
    • Traffic aggregation from multiple sources to a single monitoring tool
    • Replication of traffic streams across multiple analysis platforms
    • Flexible load balancing across tool clusters

    Advanced Traffic Filtering

    • Granular filtering based on Layer 2–Layer 4 headers
    • User Defined Byte (UDB) filtering for custom traffic selection
    • Ingress and egress filtering policies for precise traffic control
    • Template-based filtering for fast deployment and reuse

    Traffic Optimization

    • VLAN filtering, stripping, and rewriting
    • Multiple load-balancing algorithms including hash-based and utilization-based
    • Session stickiness to maintain flow integrity across tools

    Tunnel Awareness

    • GTP filtering
    • GRE termination
    • MPLS filtering and stripping
    • VXLAN filtering and stripping

    Flexible Management

    • Command Line Interface (CLI)
    • Web-based graphical interface
    • REST API for integration with orchestration platforms
    • Authentication and monitoring via TACACS+, RADIUS, SNMP, and NTP

    High Availability Design

    • Dual power supplies
    • Built for mission-critical environments
    • 3290 model - industrial temperature range

    MADE in the USA

    Niagara Networks is among the few companies designing and manufacturing network visibility solutions in the USA, ensuring quality, reliability & security compliance Learn more
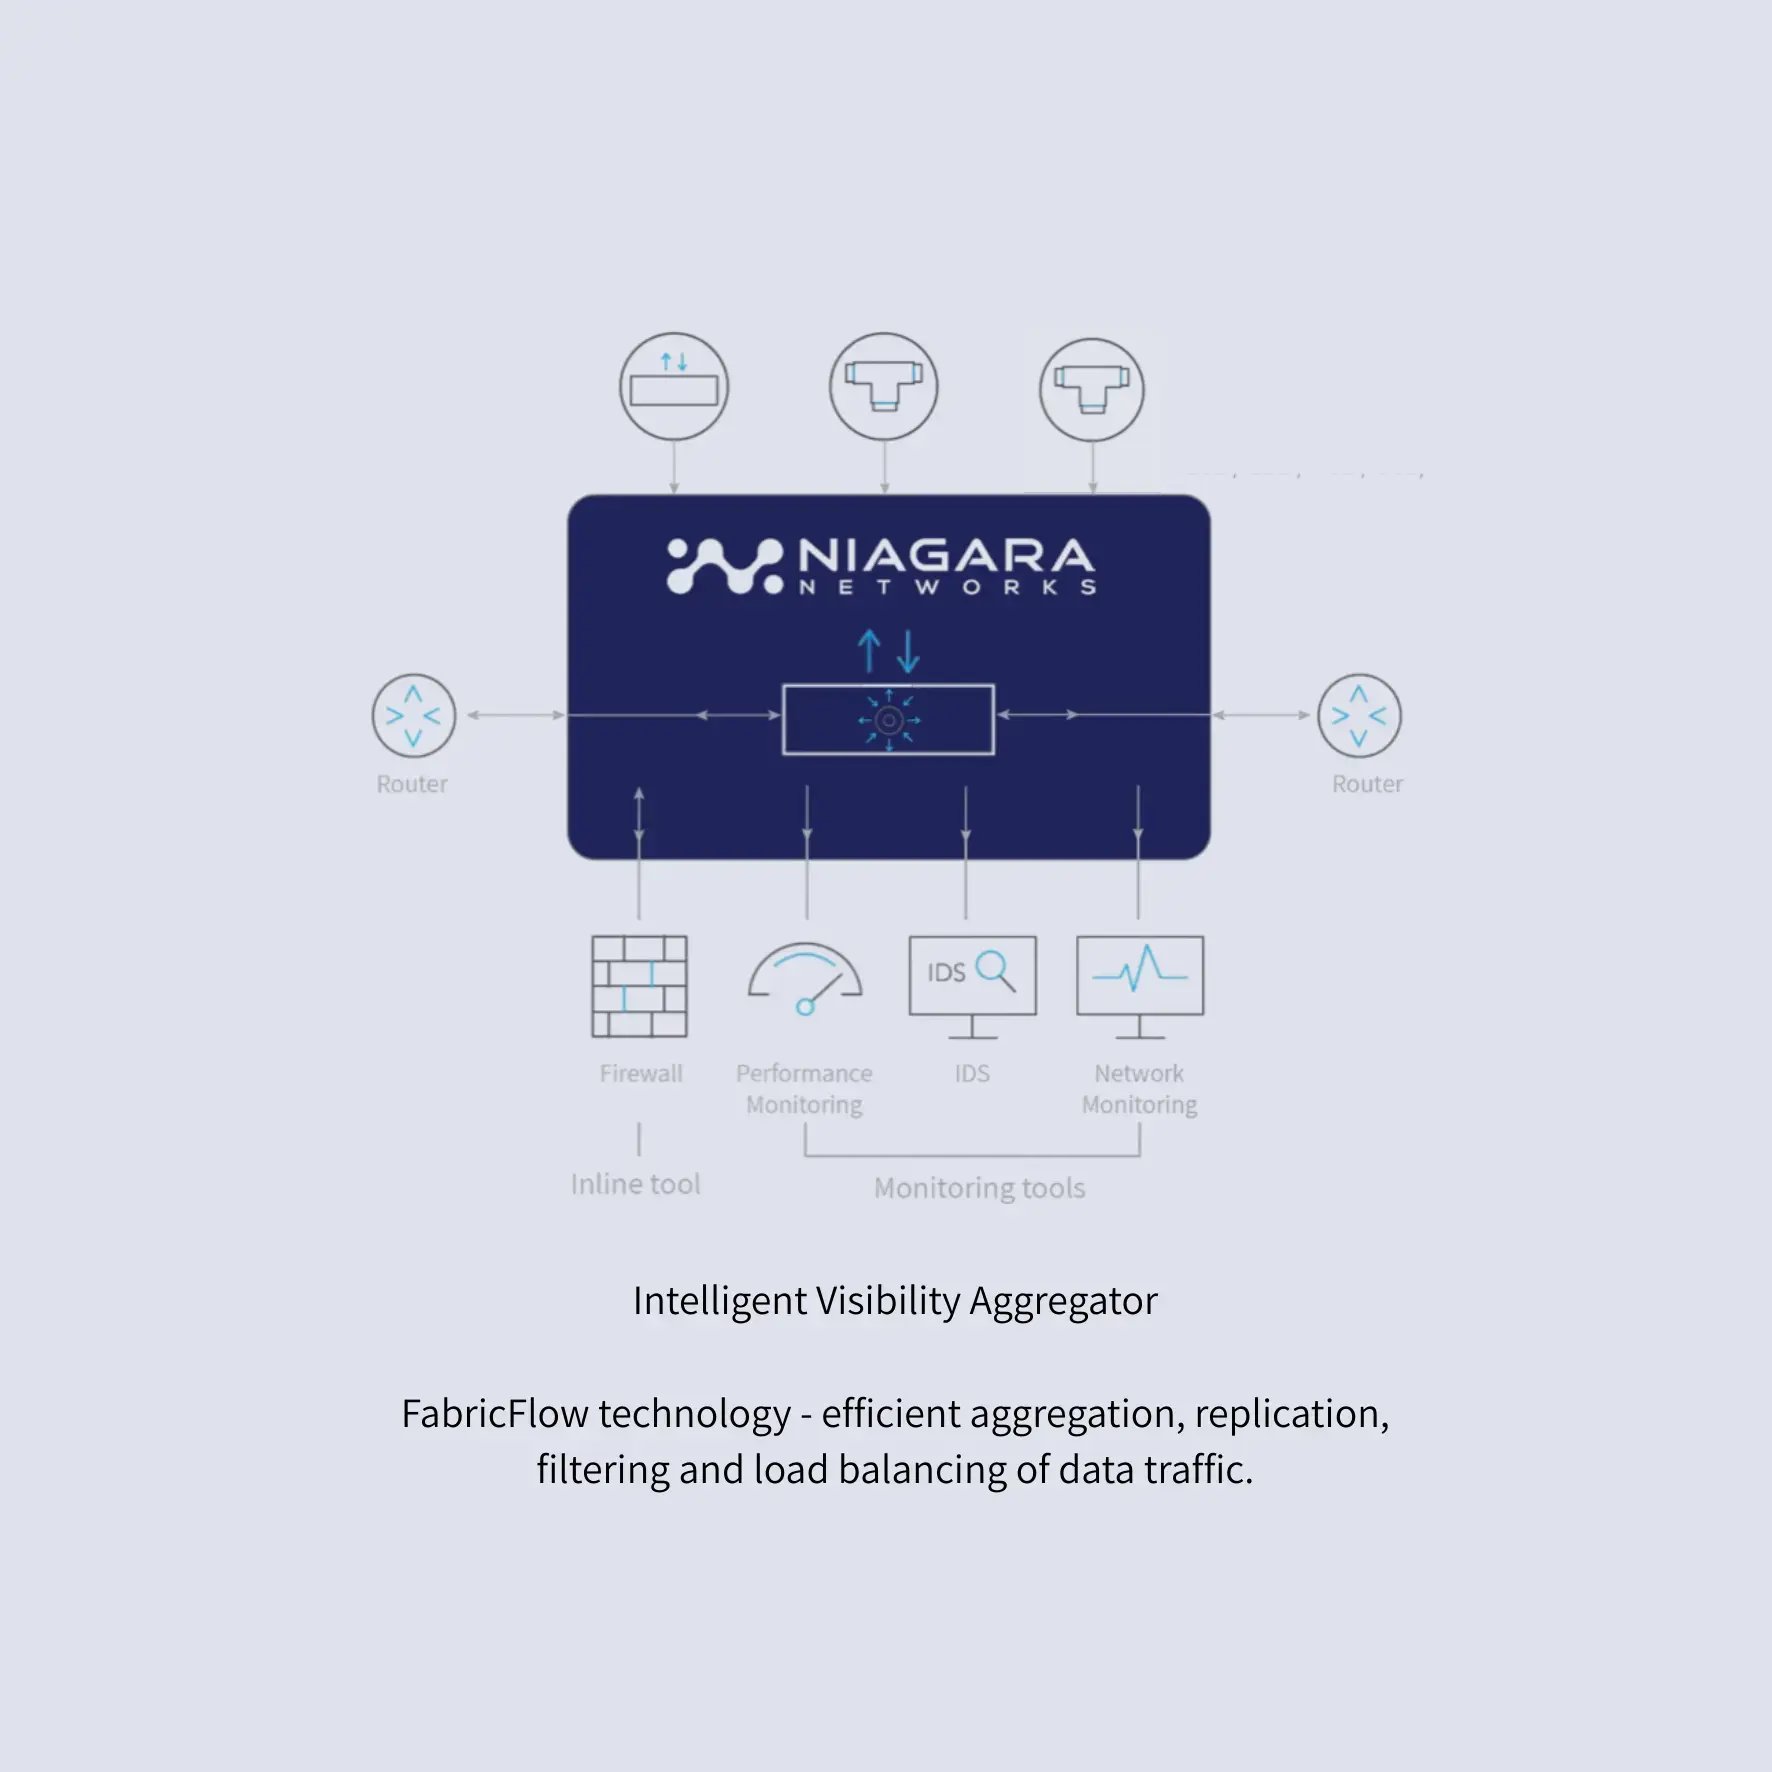
    42XX NPB aggregator

    Use Cases

    Aggregate, filter, and distribute traffic intelligently across multiple monitoring, performance, and security tools.
    Ensure efficient utilization of existing infrastructure by sending only relevant traffic to each tool.

    The 42xxE platform acts as a centralized traffic aggregation layer, consolidating traffic from multiple TAP and SPAN sources into a unified visibility fabric.

    By filtering and distributing only relevant data to monitoring and security tools, organizations can reduce tool overload, improve analysis accuracy, and simplify complex network architectures.


    Small on-premises data centers often struggle to deliver full packet visibility without adding complexity or cost. By aggregating traffic from TAP and SPAN sources and filtering only relevant packets, the compact packet brokers help organizations provide monitoring and security tools with clean, optimized data streams.

    This approach improves analysis accuracy, reduces tool overload, and enables efficient network visibility even in space- and budget-constrained environments.


    4204 | 3290 Compact Packet Broker – Frequently Asked Questions (FAQ)

    The 4204 and 3290 are compact network packet brokers designed to provide advanced traffic aggregation, filtering, replication, and load balancing. They extend network visibility to edge, remote, and industrial environments while maintaining consistent functionality with Niagara Networks’ visibility architecture.

    The 4204 is designed for high-speed edge and enterprise deployments with four 1/10Gb ports, while the 3290 is an industrial-grade packet broker with four 1Gb copper ports, optimized for harsh and remote environments.

    Both models are ideal for:

    • Distributed network visibility at remote or edge sites
    • Traffic aggregation from TAP and SPAN sources
    • Security monitoring (IDS/IPS, NDR tools)
    • Performance monitoring and analytics
    • Industrial and OT network visibility (3290 specifically)


    They aggregate traffic from multiple sources, filter out irrelevant data, and deliver optimized traffic streams to monitoring and security tools. This reduces tool overload, improves analysis accuracy, and eliminates blind spots.

    Yes. Both models support advanced filtering (Layer 2–Layer 4 and user-defined criteria), traffic replication, and multiple load-balancing methods to ensure efficient and intelligent traffic distribution.

    Yes. Both models feature a compact form factor, making them ideal for edge locations, remote sites, and environments where space and power efficiency are critical.

    The 3290 is designed for operation in harsh conditions, including extended temperature ranges and environments such as power substations, mining sites, and outdoor or industrial facilities.

    Both models support multiple management interfaces, including CLI, web-based UI, and REST APIs, along with integration capabilities using SNMP, RADIUS, and TACACS+.

    The 4204 and 3290 extend Niagara Networks’ visibility fabric to smaller-scale, edge, and industrial deployments, ensuring consistent features and operational workflows across the entire infrastructure - from core to edge to industrial networks.

    Unlock smarter visibility 

    Discover how Niagara’s Network Intelligence platform empowers NOC and SOC teams with advanced packet processing, deep traffic insight, and scalable performance across any environment.


    Fill out the form and our team will connect with you to explore how our solution can strengthen your network visibility strategy.


    Designed, Engineered & Manufactured in the USA

    From design to production, our solutions are built to the highest standards of quality, security, and performance, trusted by organizations worldwide and deployed in some of the world’s largest mission-critical networks.

    Connect with a Visibility Expert