close
close-x

Site Search

    ECH-Aware TLS 1.3 Selective Decryption

    Decrypt What Matters. Bypass What Is Private.

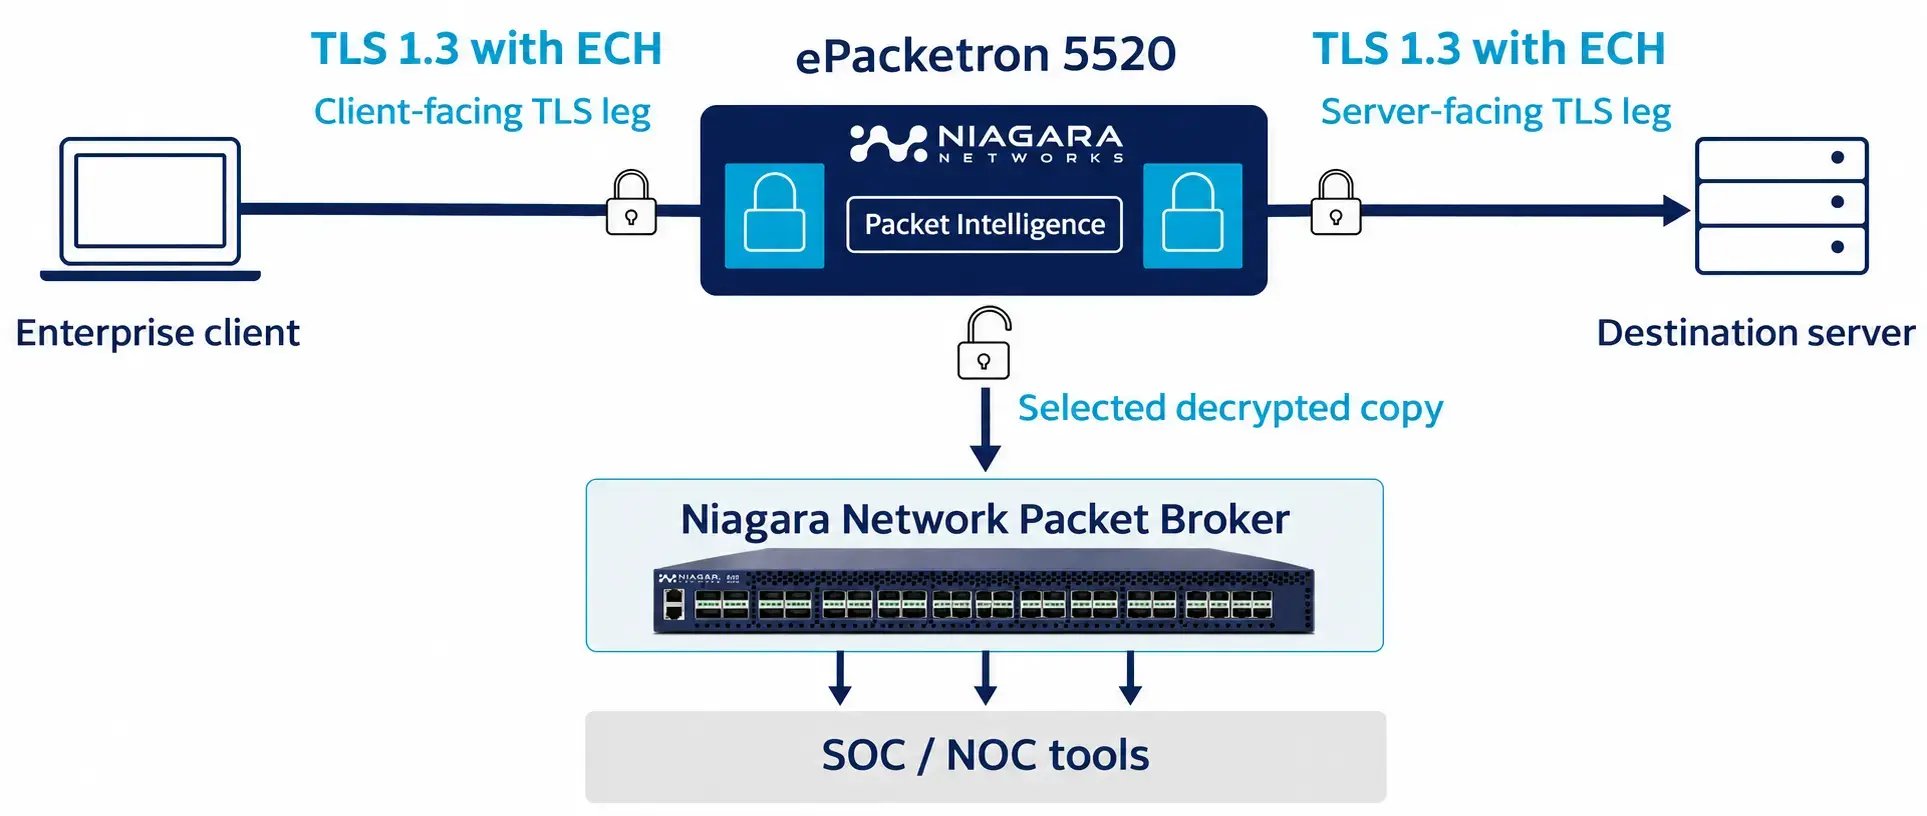
    Encrypted Client Hello (ECH) protects the destination hostname inside the encrypted TLS handshake, limiting the information available to conventional passive monitoring and hostname-based policies.

    ePacketron supports authorized, ECH-aware TLS 1.3 inspection for compatible enterprise-managed connections. Supported destination intelligence and configurable policies help security teams determine which connections to decrypt, leave encrypted, or block.


    • Inspect selectively: Apply destination categories and organizational policies to prioritize eligible traffic for security analysis.

    • Preserve sensitive communications: Leave designated privacy-sensitive connections encrypted according to configured bypass policies.

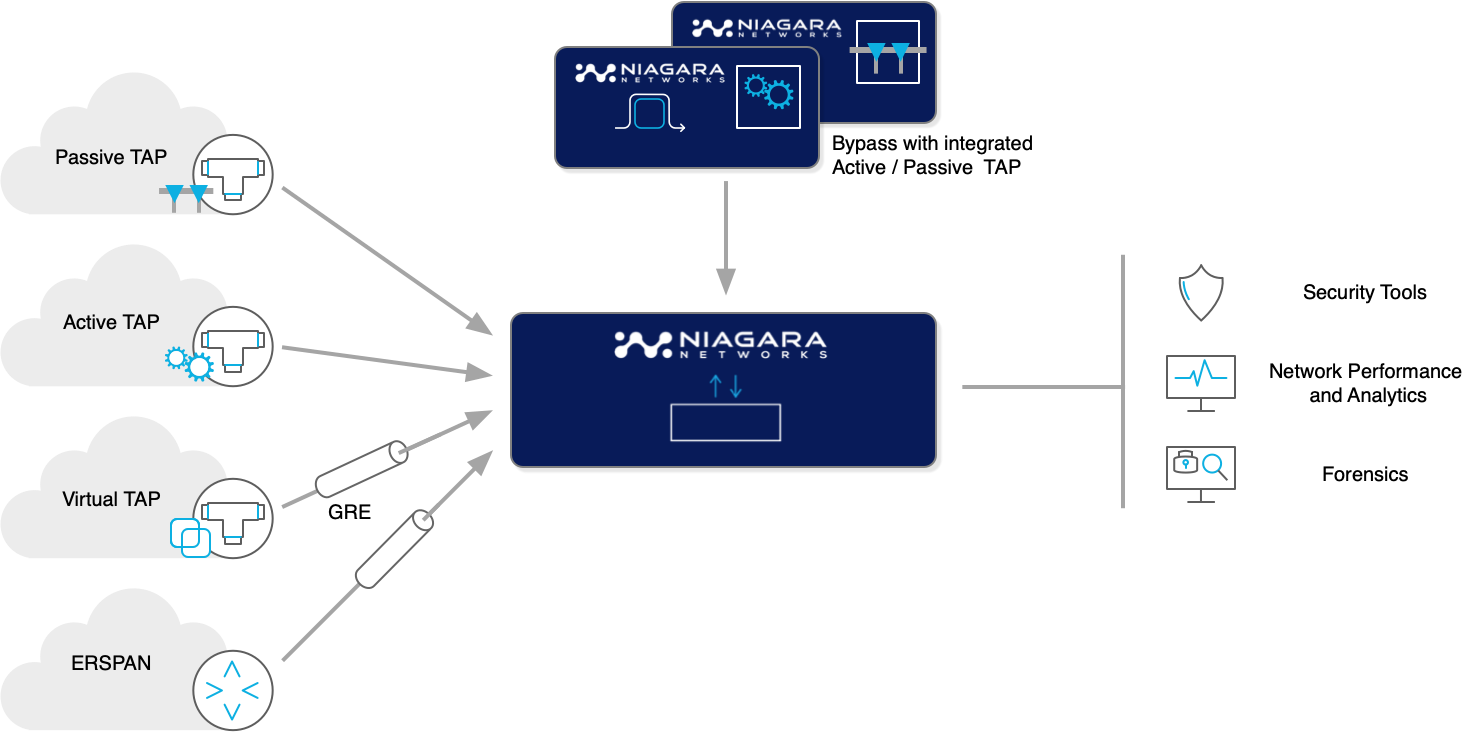
    • Decrypt once, inspect many: Deliver selected decrypted copies through Niagara Network Packet Brokers to existing security and monitoring tools.

    • Support evolving cryptography: Enable hybrid and standalone post-quantum key exchange, including X25519MLKEM768 and ML-KEM-1024, on supported client-facing and server-facing TLS connections.


    ECH-aware inspection uses active TLS interception and requires appropriate enterprise certificate trust, compatible clients, and supported deployment configurations. Each TLS leg negotiates cryptographic support with its respective peer. Applications with certificate pinning or other interception restrictions may require encrypted bypass.


    Explore ECH-aware TLS inspection


    Read more about Network Intelligence functions 
    TLS ECH-aware decryption Diagram

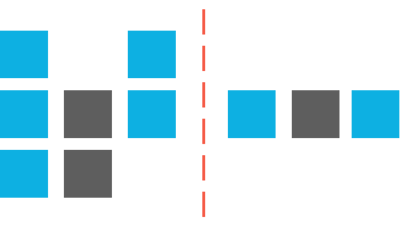
    Deduplication

    Deduplication identifies and removes duplicate packets before sending them to a network appliance. While duplicate packets may occur in backup and failover deployment architectures, the more common cause is using multiple SPAN ports across connected switches and routers that feed into a network appliance. When a network appliance handles duplicate packets, they consume the tool's limited processing resources, which degrades the overall performance and potentially affects the accuracy and reported results. Read more about Network Intelligence functions 

    Packet Deduplication

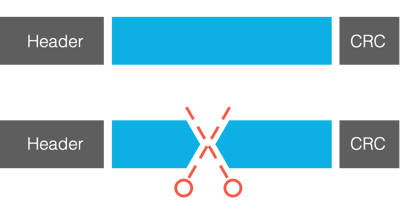
    Packet Slicing

    Packet Slicing services reduce the volume of data to be forwarded for analysis and processing by shortening packet length. It’s useful for network applications which require only header analysis and/or a defined set of bytes from each packet. User-configurable rules reduce the packet length.

    Read more about Network Intelligence functions 

    Packet slicing

    NetFlow/IPFIX and metadata

    Traffic capacity is increasing as is the need for greater processing granularity; together these make many network tools ingest traffic metadata rather than raw traffic packets. Often, the network element itself generates metadata reports, such as a switch or a router. 
    The problem is that because metadata generation isn't the switch’s or router’s primary objective, metadata performance may degrade during congestion. Also, in an effort to compensate, the device resorts to traffic sampling instead of accounting for every packet in the flow. Niagara’s solution avoids both problems. 

    Read more about Network Intelligence functions 

    Netflow IPFIX

    Data Masking

    Data Masking lets your company forward and share data traffic across departments while masking private and confidential user information.

    Read more about Network Intelligence functions 

    Data masking

    Application Filtering

    Identification of applications and Layer 7 protocols often requires deep packet inspection and analysis. Application filtering performs DPI and supports identifying dozens of applications. The supported application list is updated regularly.

    Read more about Network Intelligence functions 

    Application L7 filtering

    Tunnel Support

    Tunnel Support encapsulates traffic and forwards it to a remote or central location. It can also terminate tunnels and forward the decapsulated (de-tunneled) traffic to network tools.

    Read more about Network Intelligence functions 

    Tunnel Support

    GTP Correlation

    GTP, or GPRS Tunneling Protocol, carries user data across mobile networks.

    One of the main challenges for network tools in mobile networks is that the user plane and control plane are decoupled. This happens for performance, monitoring, behavioral analysis, as well as other analysis that requires differentiating user traffic. To understand and identify a specific user’s traffic, network tools must correlate it with the control/signaling plane. GTP Correlation includes multiple applications that boost network tool connectivity in mobile environments. Other associated applications include optimized load balancing based on user traffic, IMSI filtering, and more.

    Read more about Network Intelligence functions

    Header Stripping

    Header Stripping streamlines and modifies traffic at the network edge so the intended network tool can process it and fulfill its purpose. Niagara’s application will strip the header from the traffic, exposing the relevant packet for processing.

    Read more about Network Intelligence functions

    Packet Header slicing - stripping

    Regex

    Regex Patterns extend existing filtering and data masking features while adding new modes of operation. The user can define any pattern through a regular expression, or load a predefined expression. This feature lets the user perform advanced packet filtering, masking, and session filtering.  Regarding session filtering, once the pattern is detected in any packet, the entire session is found and can be filtered. For every pattern match, the user can configure it to filter or to exclude the match.

    Read more about Network Intelligence functions 

    Regular Expression search - REGEX

    ePacketron-powered Network Intelligence Applications reduce tool load, simplify training, improve risk management, access management, digital infrastructure management, and optimize SOC/NOC workflows, as demonstrated in our real-world case study.