close
close-x

Site Search

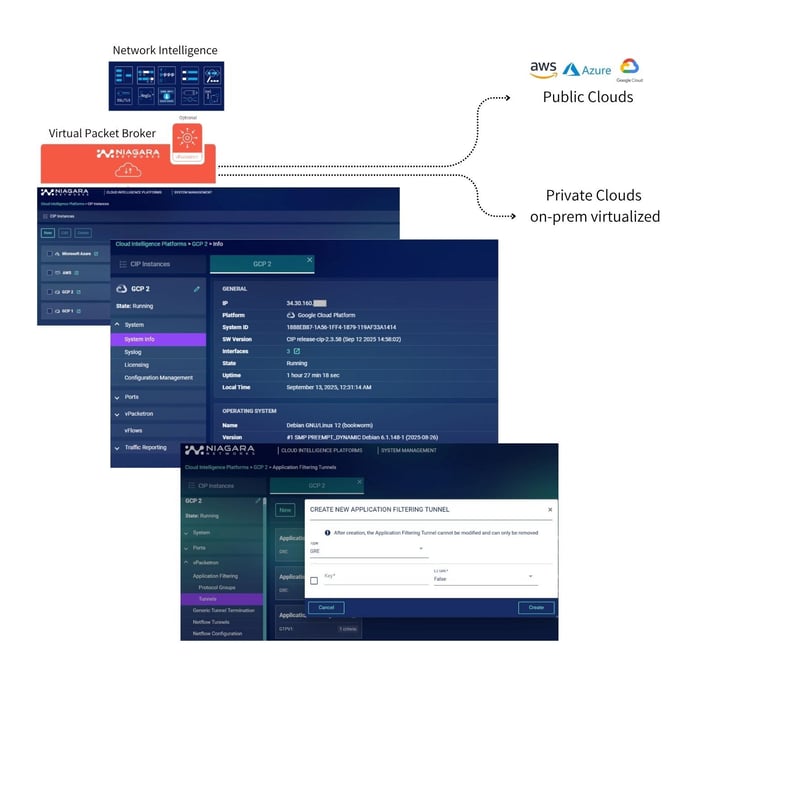
    CIP diagram - enable packet intelligence in hybrid cloud

    Cloud-Native Visibility, Delivered Everywhere...


    A cloud-native visibility layer that monitors, filters, and enriches traffic across AWS, Azure, GCP, and virtualized data centers.

    Cloud Intelligence Platform (CIP) is a cloud-native virtual packet broker that delivers full packet-level visibility across hybrid and multi-cloud environments. It bridges public clouds and private on-prem virtualization, providing smart filtering, traffic optimization, tunnel handling, and advanced Layer-7 intelligence.  

    With centralized management and elastic cloud scalability, CIP ensures SOC, NOC & cloud teams always receive the right traffic, at the right time, with full context.

    CIP - Packet Data Intelligence

    A unified virtual packet broker that scales with your cloud workloads and delivers real-time traffic intelligence anywhere.


    Intelligent
    • Application-aware filtering

    • Layer-7 enrichment

    • TLS/metadata inspection*

    Adaptive
    • Auto-scales with cloud workloads

    • Fits any cloud architecture

    • Dynamic traffic steering

    Unified
    • Works across AWS, Azure & GCP

    • Integrates with private & on-prem virtualization

    • Flexible policy profiles & unified
      control layer

    Scalable
    • High-throughput virtual architecture
    • Multi-region, multi-VPC visibility
    • Tool load optimization
    CIP - You Can't Secure, Optimize, or Monitor Traffic you Can't See

    Why Cloud Intelligence Platform Is Required in Modern Virtualized Cloud Environments?

    Traditional packet brokers were designed for predictable, box-based networks.
    Cloud networks are dynamic, on-demand, multi-layered, and use overlay tunneling (VPC/VNet, VXLAN, GENEVE, GRE), making traffic flow opaque to security and performance tools.

    In virtualized and cloud-native networks:

    • Traffic is highly distributed across availability zone, subnets, and regions
    • East–West traffic grows and becomes harder to tap
    • Cloud-native services use encapsulation (VXLAN/GENEVE) and micro-service routing
    • Tools must ingest only the right traffic, not full packet copies
    • VMs, containers, and server-less workloads have short lifecycles
    • Cloud providers limit or block access to the raw packet plane
    • This means traditional TAPs, SPAN ports, and physical packet brokers cannot operate where the traffic actually lives

    CIP solves the core challenge of visibility in virtualized, multi-cloud networks:

    Built for Cloud-Native Overlay

    CIP is built specifically for cloud environments that operate at speed, scale and elasticity

    Close to Workloads

    CIP engines run close to workloads, applying L2–L7 processing locally without moving traffic across the cloud

    Traffic Reduction Before Sending to SOC/NOC Tools

    Eliminating duplicates, irrelevant packets, unnecessary tunnels, noisy flows & reducing payload size through packet slicing. CIP also handles encrypted traffic with optional TLS decryption*, resulting in lower tool overhead and faster investigation times

    Cloud-Native Compliance & Segmentation

    Operate visibility virtual toolkit within the same trust boundary as the cloud application. No exporting raw traffic across accounts or regions unless policy-approved by SOC/NOC and cloud operations teams

    You Can't Secure, Optimize, or Monitor Traffic you Can't See...

    CIP gives cloud, NetOps, and SOC teams a virtual packet broker layer purpose-built for distributed cloud architectures - bringing packet intelligence back into environments where traditional solutions cannot reach

    Elastic, Event-Driven Scaling

    CIP scales with cloud workload changes - spinning up more engines during traffic spikes & scaling down when idle, enabling efficient TCO through an agile, cloud-native software architecture

    Inspect, Monitor, and Control Packets Across 
    Hybrid Cloud  Environments

    Cloud Intelligence Platform (CIP) delivers deep packet-level visibility across hybrid cloud environments, ensuring complete insight for security and performance operations

    Cloud-Native Visibility

    • Deploys seamlessly in AWS, Azure, GCP, and private clouds

    • Supports hybrid, multi-cloud, and virtualized infrastructures

    • Scales elastically with cloud workloads and tool requirements

    Advanced Layer-7 Network Intelligence

    • Application-aware filtering for precise traffic delivery

    • Regular expression filtering for deep content matching

    • Optional TLS decryption for secure traffic inspection*

    • Subscriber-aware mobile visibility (3G/4G/5G)

    Traffic Optimization & Control

    • Packet and flow slicing to reduce load on downstream tools

    • Deduplication to eliminate redundant packets & false positives 

    • Generic header stripping for efficient packet processing

    • NetFlow/IPFIX export for flow-level analytics

    Smart Traffic Distribution

    • Intelligent filtering, aggregation, replication & load balancing

    • Full tunnel termination for GRE, VXLAN, NVGRE, GENEVE & ERSPAN 

    • Header stripping for VNTag, VLAN/QinQ, FabricPath, MPLS, PPPoE, ERSPAN, GTP-U and Cisco Ttag, enabling clean tool-side delivery

    Centralized Management & Automation

    • Role-based access control with a unified web interface

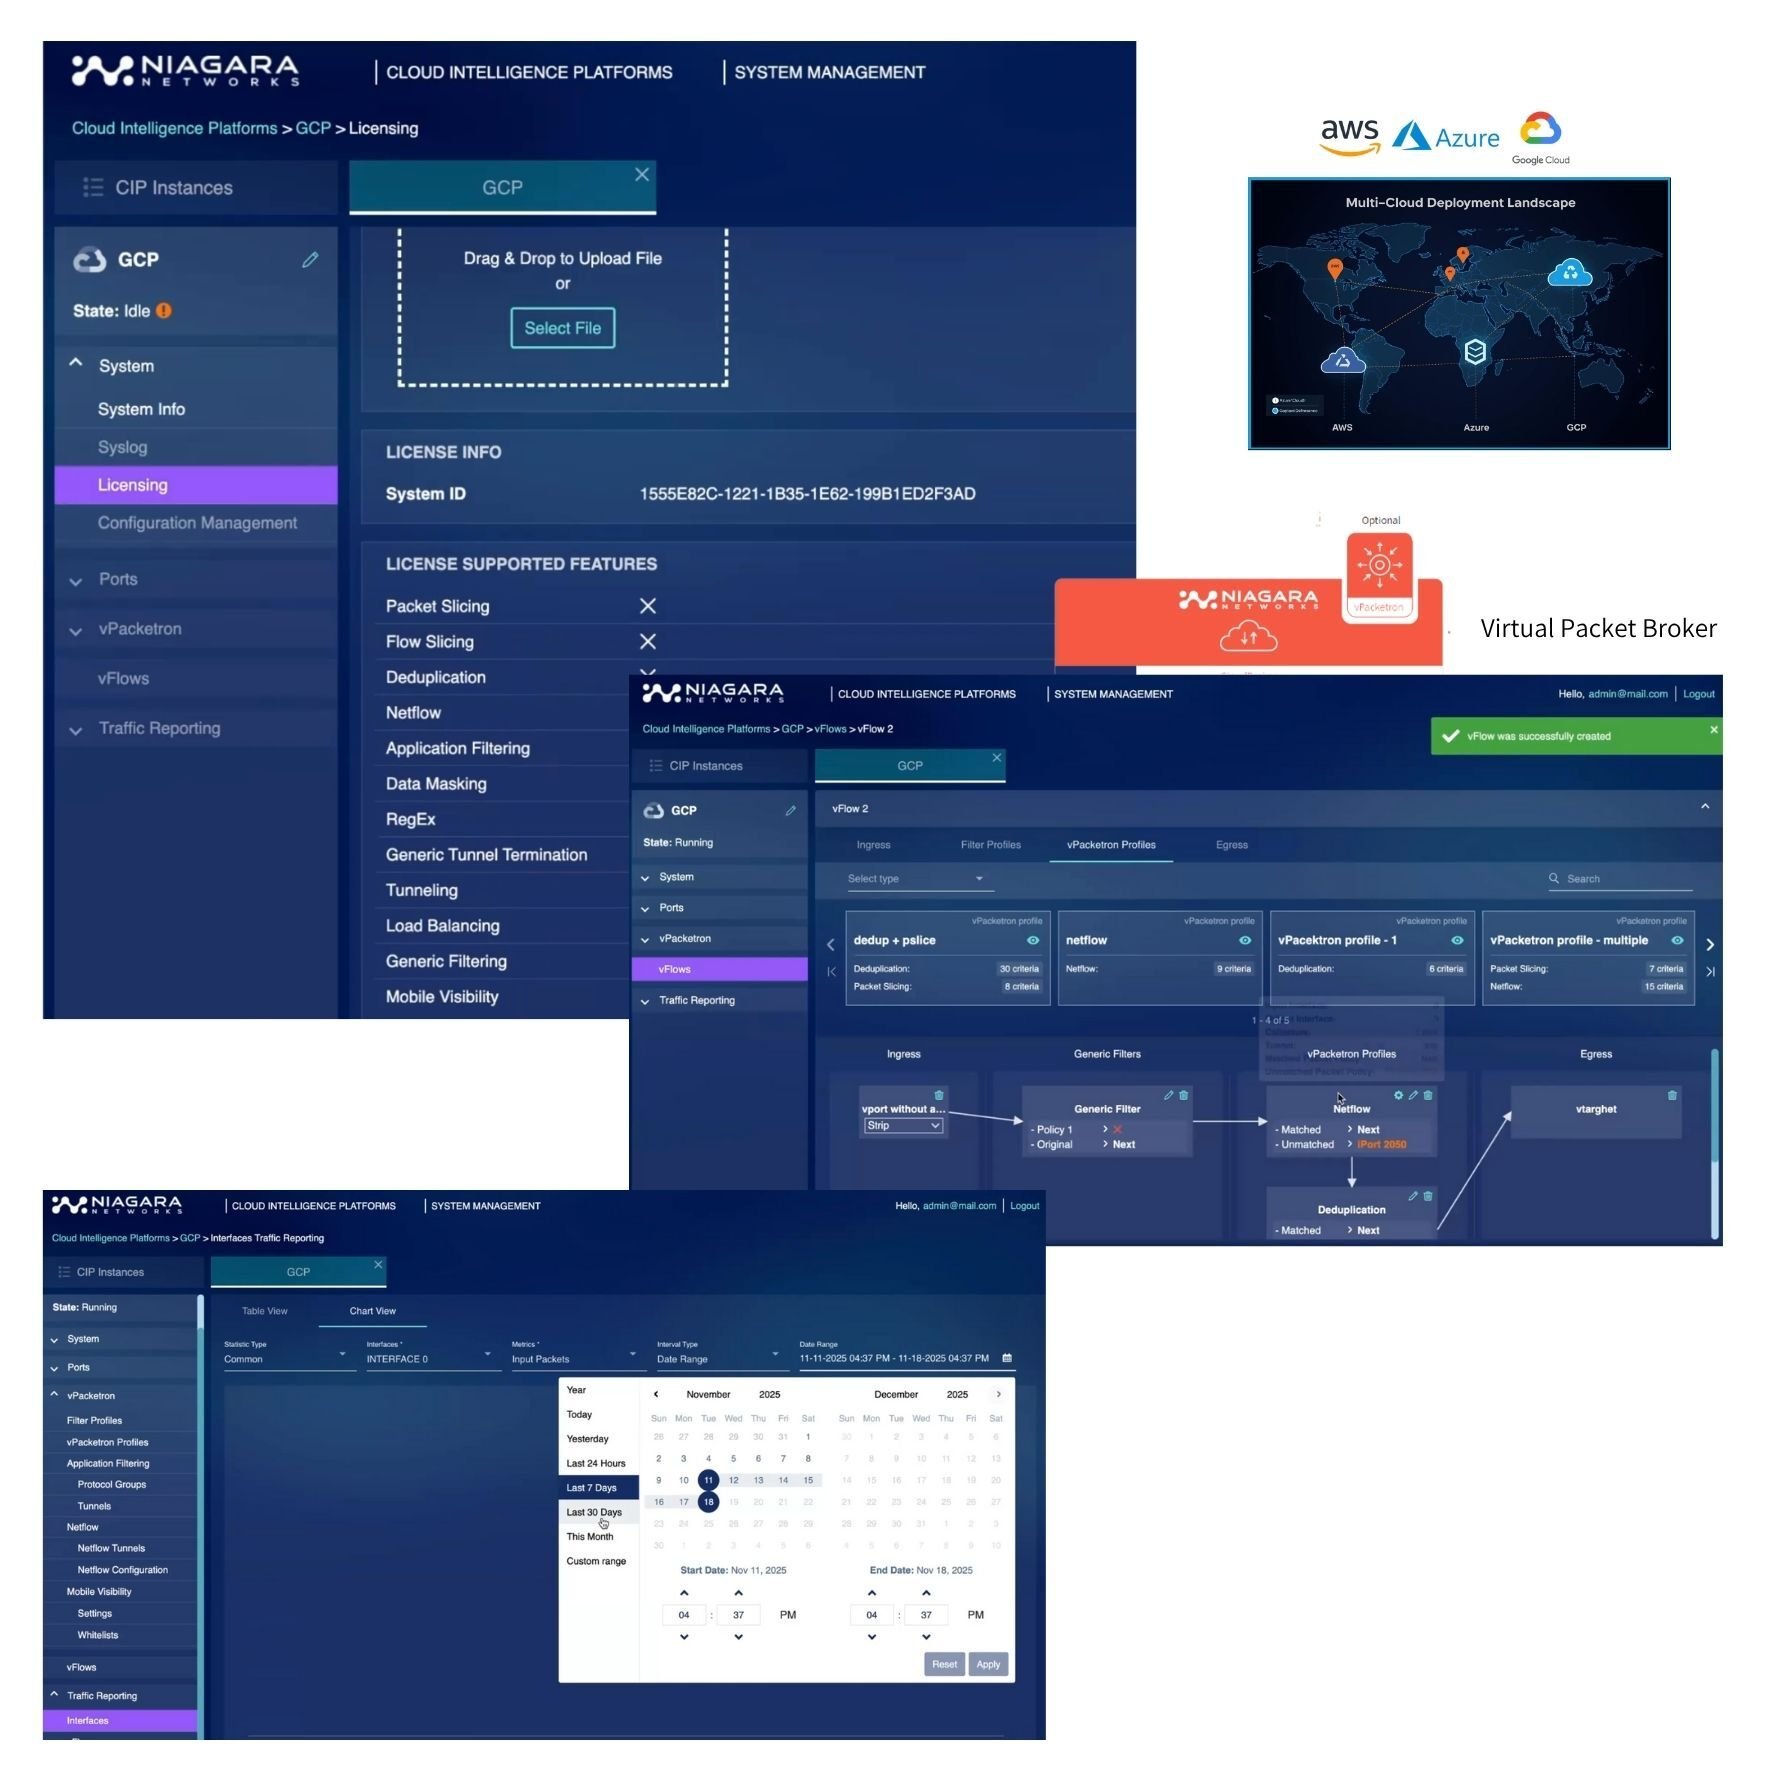
    • CIP combines a central controller with distributed engines to manage virtual packet processing across cloud environments
    • Simple provisioning across multiple cloud regions and VPCs

    High-Performance Virtual Architecture

    • Supports up to 60 vPorts per virtual interface

    • High-throughput packet processing using DPDK/SR-IOV

    • Elastic resource scaling with cloud-native compute
    CIP - USE CASES - THE ULTIMATE SOLUTION FOR HYBRID CLOUD

    Use Cases

    In today's fast-paced digital world, businesses are embracing the benefits of hybrid cloud environments. However, as these environments become more complex, it's essential to have a comprehensive view of network traffic across your entire infrastructure - on-prem, private cloud, and public cloud environments. That's where cloud packet brokers come in. 

    Close cloud visibility gaps, optimize SOC/NOC tools with cleaner traffic, enhance mobile and virtual network insight, and ensure secure, seamless cloud operations.
    Spyware and zero-day attacks are designed to be invisible, but with strong network visibility, they increase the chances of early detection and effective response. Visibility is a foundational layer, but pairing it with effective analysis and rapid response is essential to neutralize threats. By strategically using modern security tools and maintaining comprehensive monitoring, organizations can reduce their vulnerability and defend against today’s most sophisticated cyber threats.

    "We needed an absolutely perfect packet collection system - not just fault-tolerant, but fault-free - and Niagara solution provided that."

    - Data Analysts -


    Continuous monitoring is a core requirement of the NIST Cybersecurity Framework 2.0, ensuring that adverse events are detected early and acted upon before they escalate. Traditional methods such as SPAN ports or mirroring are no longer sufficient for today’s high-bandwidth and hybrid environments, where blind spots and encrypted traffic can mask threats.
    Niagara Networks addresses this challenge by delivering complete, real-time visibility across physical, virtual, and cloud infrastructures.
    With advanced capabilities such as inline bypass, TLS decryption, packet slicing, and traffic aggregation, Niagara enables NetOps and SecOps teams to continuously monitor all traffic flows, detect anomalies, and ensure compliance. This visibility directly supports
    the Detect (DE.CM) category of NIST CSF 2.0, helping organizations monitor networks, external services, and computing resources
    without compromise.

    Cloud Intelligence Platform – Frequently Asked Questions (FAQ)

    CIP is a cloud-native virtual packet broker that provides deep packet-level visibility, filtering, and traffic optimization across public, private, and hybrid cloud environments.

    CIP supports AWS, Azure, GCP, VMware ESXi, KVM, OpenStack, Hyper-V*, and private on-prem virtualization platforms. It can operate in multi-cloud and hybrid cloud deployments.

    CIP offers packet filtering, aggregation, replication, load balancing, tunnel termination (GRE, VXLAN, GENEVE, ERSPAN, NVGRE), de-duplication, packet and flow slicing, header stripping, NetFlow/IPFIX generation, application filtering, data masking, RegEx filtering, and optional TLS decryption.

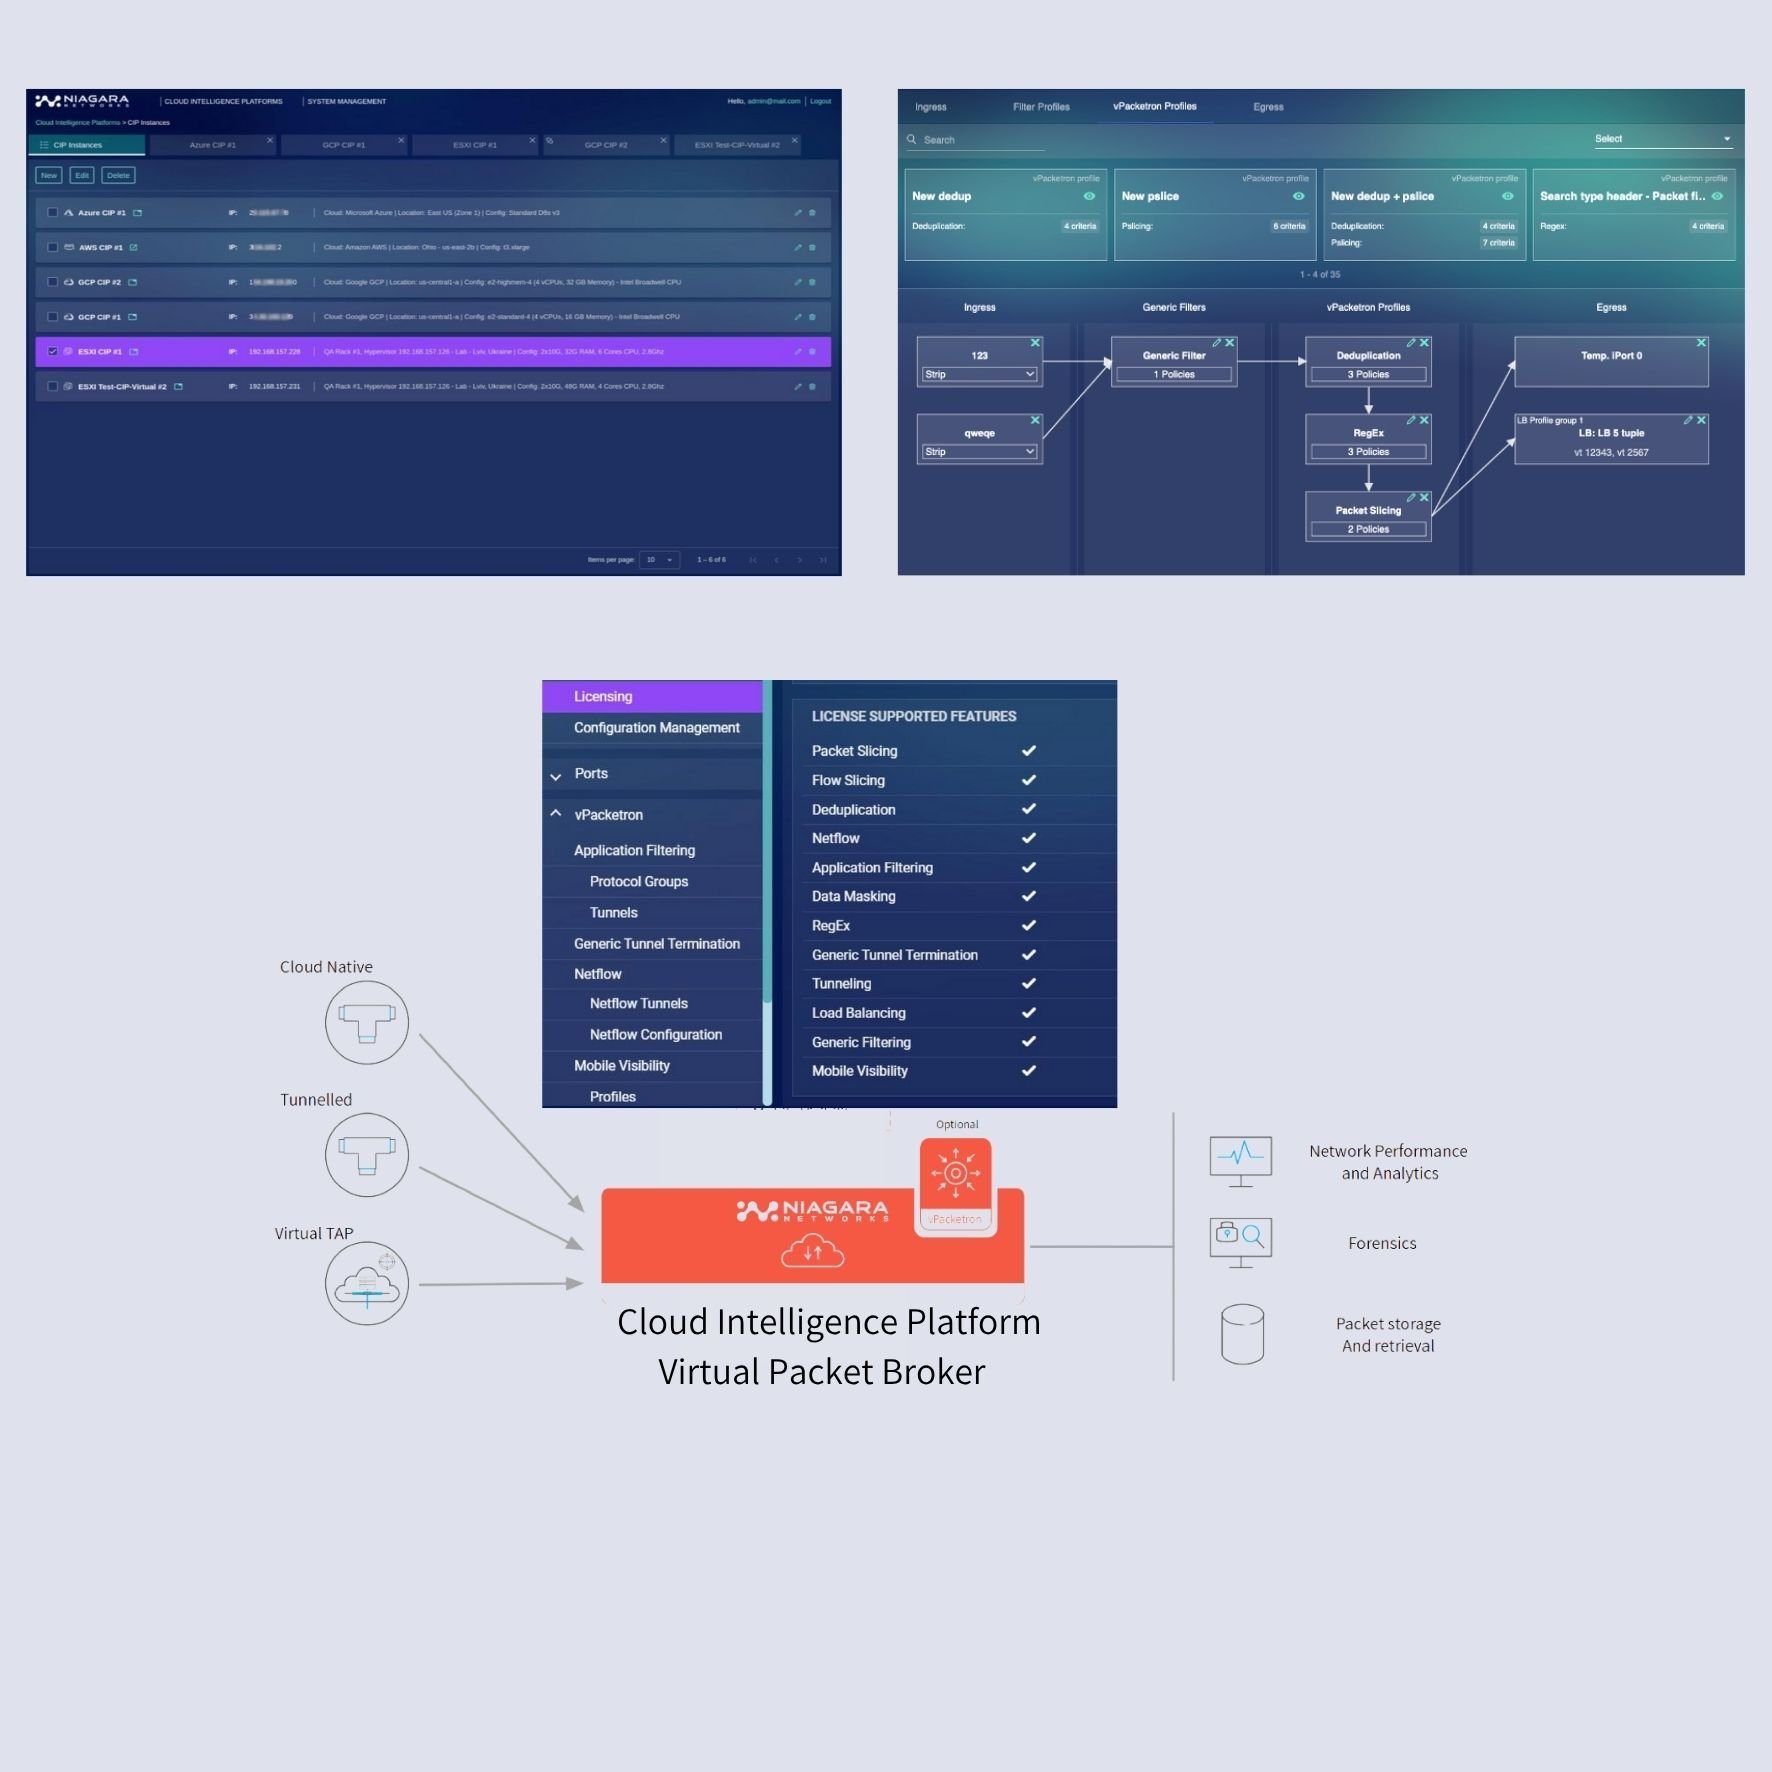
    CIP can ingest tunneled traffic from remote on-premises physical TAPs or SPAN ports using standard tunneling protocols, as well as traffic mirrored from any third-party virtual TAP or cloud-native mirroring service. The platform supports multiple delivery methods, ensuring highly efficient collection and aggregation of traffic from diverse sources - whether originating from on-premises infrastructure, private data centers, or hybrid cloud environments.

    vPacketron adds advanced Layer-7 network intelligence such as deduplication, slicing, application filtering, mobile subscriber visibility (3G/4G/5G), and enriched metadata extraction to optimize SOC/NOC traffic analysis.

    As part of the future software release, CIP will offer optional TLS decryption* as well as metadata-based inspection through application filtering, SNI/URL filtering*, and protocol reporting*.

    Yes. Features like deduplication, flow slicing, packet trimming, and application filtering reduce noise and tool overload, lowering processing, storage, and cloud compute costs.

    CIP is deployed as a virtual appliance. The CIP Controller then discovers and manages all instances across cloud accounts, VPCs, and virtual networks.

    The CIP Controller provides:

    • Centralized web UI across all CIP instances

    • Unified templates and configuration management

    • Role-based access control

    • Central policy updates across multi-cloud environments

    Yes. CIP supports elastic scaling through cloud-native resources, high-performance packet processing (DPDK/SR-IOV), and multi-instance coordination via the CIP Controller.

    Yes. CIP works seamlessly with Niagara’s physical TAPs and packet brokers to deliver unified visibility across hybrid infrastructures. For a detailed comparison of all Niagara physical appliances, please visit the product comparison page. 

    CIP (Cloud Intelligence Platform) and CIT (Cloud Intelligence TAP) form a unified cloud-native visibility architecture. CIT captures East-West, inter-VM, and cloud-native traffic that traditional TAPs cannot access, then forwards only the relevant, filtered packets to CIP. The CIP virtual packet broker then aggregates, processes, optimizes, and distributes this traffic to SOC/NOC tools using advanced functions such as slicing, deduplication, tunnel termination, and load balancing.
    Together, CIP + CIT provide end-to-end visibility across private, public, and hybrid clouds - from traffic capture (vTAP) all the way to traffic intelligence and delivery (virtual packet broker). This synergy ensures complete observability, lower tool load, improved security investigations, and consistent visibility even as workloads scale or migrate across cloud environments.

    Because cloud networks generate large volumes of distributed traffic, a vTAP alone is not enough. CIT delivers granular visibility at the workload level, while CIP transforms that raw traffic into actionable, optimized data streams for tools. Without CIP, tools may receive excessive or unstructured data; without CIT, tools may miss hidden traffic inside hypervisors or cloud overlays. Combined, they eliminate blind spots and provide precise, cloud-native traffic intelligence.

    All release notes, guides & supported environment documents are available through the Niagara Networks Support Portal.

    Unlock smarter visibility 

    Discover how Niagara’s Network Intelligence platform empowers NOC and SOC teams with advanced packet processing, deep traffic insight, and scalable performance across any environment.


    Fill out the form and our team will connect with you to explore how our solution can strengthen your network visibility strategy.


    Designed, Engineered & Manufactured in the USA

    From design to production, our solutions are built to the highest standards of quality, security, and performance, trusted by organizations worldwide and deployed in some of the world’s largest mission-critical networks.

    Connect with a Visibility Expert