close
close-x

Site Search

    ePacketron - Network Intelligence

    ePacketron Packet Deduplication

    Packet deduplication identifies and removes duplicate network packets before they reach security and monitoring tools. ePacketron 5520 performs deduplication in the visibility layer at up to 450 Gbps aggregate IMIX throughput per appliance, to help SOC and NOC teams reduce tool load, storage use, packet drops, and investigation noise.


    High-Performance Deduplication at 450 Gbps Throughput per Appliance

    Modern SOC/NOC teams rely on complete packet visibility, but duplicate packets can create unnecessary noise, consume expensive tool capacity, increase storage requirements, and slow down investigation workflows.


    Niagara Networks' ePacketron brings high-performance Packet Deduplication directly into the visibility layer and removes duplicate packet copies before they reach downstream security and monitoring tools.


    With up to 450 Gbps aggregate IMIX throughput per appliance, ePacketron lets enterprise and service provider environments clean, optimize, and deliver traffic at scale, freeing tools to focus on the packets that matter.


    Niagara Networks transforms network visibility into a managed traffic intelligence platform where the right traffic is secured, optimized for each tool and then shields key networks against blind spots and downtime.


    Deduplication

    Collect the Right Traffic

    Capture complete packet data from physical, virtual, cloud, and hybrid environments using TAPs, virtual TAPs, and hybrid bypass access points.

    Optimize It Intelligently

    Use packet brokers and ePacketron network intelligence to filter, deduplicate, slice, decrypt, replicate, and load-balance traffic before it reaches your tools.

    Deliver It with Confidence

    Feed SOC/NOC, monitoring, and security platforms with reliable, policy-driven traffic while protecting uptime across mission-critical networks.

    The Problem: Duplicate Packets Drain Tool Capacity

    In today’s visibility architecture, SPAN ports, TAP aggregation, failover architectures, multipoint monitoring, and complicated data center architecture frequently create duplicates. Duplicate packets happen when multiple tap and aggregation points across the data center collect the same traffic, creating redundant copies. When these duplicated packets get sent to monitoring and security tools, they can create several operational challenges:


    • Lower effective tool capacity

    • Increased storage consumption for packet capture and forensic analysis

    • A higher risk of packet drops on analyzers
    • Time-consuming investigation and troubleshooting cycles
    •  Increased noise for SOC/NOC teams
    •  Less ROI from existing security and monitoring infrastructure


    The impact to a business's operations is clear: tools waste resources analyzing duplicate traffic which could have been used for detection, analysis, compliance, and performance monitoring. Duplicate packets can impact security infrastructure efficiency significantly, particularly when traffic from various sources converges to monitoring points.


    The ePacketron Approach: Deduplication in the Visibility Layer

    ePacketron moves Packet Deduplication into the Network Intelligence layer before traffic has the chance to reach the tools. As opposed to making each downstream tool deal with duplicate packet information, ePacketron eliminates duplicate traffic in the visibility layer and delivers only relevant traffic flows to SOC/NOC tools. Your business will be able to optimize tool utilization, reduce excess volume of traffic, and increase the lifespan of your current investments in monitoring and security tools. ePacketron processes inbound and outbound traffic to ensure unique packets arrive at your tools.


    Performance That Fits High-Speed Networks

    Packet Deduplication is not only a feature. At very high speeds, it has to work without becoming a bottleneck. The ePacketron 5520 appliance delivers hardware-based, fine-grained support for deduplication of redundant packets before they reach analysis or security tools.

    450 Gbps

    Packet Deduplication

    Throughput per appliance

    450 Gbps

    Header-Only Deduplication

    Throughput per appliance

    IMIX

    Aggregate Traffic

    Tested with aggregate IMIX traffic

    This performance level enables deduplication to scale across high-bandwidth enterprise, data center, and service provider environments.

    Note: Performance based on aggregate IMIX traffic per ePacketron 5520 appliance.

    Key Benefits

    Improve Tool Efficiency

    Eliminate all redundant traffic prior to reaching NDR, IDS, packet capture, monitoring, and forensic tools. Duplicate packets can waste valuable processing cycles that should be dedicated to threat detection.

    Reduce Tool Overload

    Deliver cleaner traffic streams so downstream platforms can use their processing capacity more effectively. By eliminating duplicates, you reduce the volume of traffic tools must process.

    Optimize Storage

    Avoid wasting packet capture and compliance storage on duplicate data.

    Reduce Packet Drops

    Lower the load on network analyzers and monitoring platforms by filtering duplicate traffic earlier in the architecture.

    Accelerate Troubleshooting

    Reduce unnecessary packet noise and help teams focus faster on the real traffic needed for investigation and root-cause analysis. During source and destination analysis of traffic patterns, deduplication makes sure you examine unique flows.

    Extend Existing Tool Lifespan

    Improve the efficiency of current SOC/NOC infrastructure without immediately overbuilding or replacing downstream tools.

    Where ePacketron Deduplication Delivers Value

    ePacketron Packet Deduplication is designed for high-performance visibility environments, including:

    • Network forensics

    • NDR/IDS optimization

    • Packet capture optimization

    • Compliance logging

    • Storage reduction

    • SOC/NOC traffic optimization

    • Data center and service provider visibility architectures

    • Multi-point TAP/SPAN aggregation environments where traffic from multiple sources creates duplicates.

    Why It Matters

    As network speeds continue to increase, security and monitoring tools cannot afford to waste processing resources on duplicate packets. ePacketron moves advanced packet processing into the visibility layer, where it can clean and optimize traffic before it reaches key tools.


    The result is a more efficient visibility architecture, better tool utilization, and stronger operational performance across SOC/NOC environments. By properly deduplicating ingress and egress traffic, you can handle higher traffic volumes without overloading your security infrastructure.

    Turn Duplicate Traffic into Optimized Visibility

    With 450 Gbps Packet-Deduplication performance per appliance, Niagara Networks' ePacketron eliminates redundant traffic before it impacts your tools. Our solution helps remove duplicates and optimizes packets based on source and destination characteristics. ePacketron gives you cleaner visibility with less noise.

    Clean the traffic. Reduce the noise. Extend your tools.

    Niagara Networks End-to-End Visibility Solution


    Visibility Layer


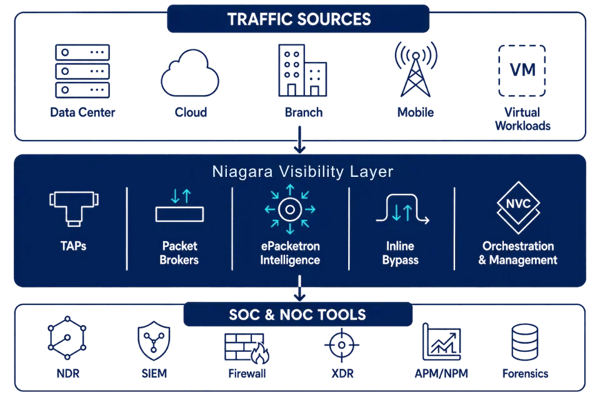
    Niagara Networks visibility portfolio helps IT teams move from fragmented monitoring feeds to a managed visibility layer. From data centers, cloud, branch, mobile, and virtual workloads, Niagara captures, optimizes, protects, and delivers traffic to SOC and NOC tools through one scalable visibility architecture. Visit Niagara Networks Appliance Comparison Matrix


    Use Niagara TAPs

    Capture traffic from critical physical links across copper, fiber, optical, passive, active, and bypass deployments. Explore Niagara Network TAPs

    Use Niagara Packet Brokers

    Aggregate, filter, deduplicate, replicate, and load balance traffic for multiple security and monitoring tools. Explore Niagara Network Packet Brokers

    Use Niagara Hybrid TAPs and Bypass Solutions

    Protect inline security tools with failover architectures that maintain continuous traffic flow and high availability. Explore Niagara Hybrid TAPs and Bypass Solutions

    Use Niagara ePacketron Network Intelligence

    Restore encrypted traffic visibility with SSL/TLS decryption and offload advanced packet processing, including application filtering, packet slicing, deduplication, NetFlow/IPFIX, data masking, and traffic optimization. Explore ePacketron Network Intelligence

    Use Niagara Virtual TAPs & Virtual Packet Broker

    Extend visibility into virtualized and cloud environments, capturing east-west traffic and optimizing virtual traffic delivery where physical TAP deployment is not possible. Explore Niagara Virtual TAPs and Virtual Packet Broker

    Use Niagara Visibility Orchestration

    Simplify provisioning and centralized policy management across the entire visibility layer. Explore Niagara Visibility Orchestration
    Clean the traffic. Reduce the noise. Extend your tools.

    Plan network packet deduplication for your traffic

    Share your TAP or SPAN sources, sustained and peak traffic rates, estimated duplicate traffic, and the capacity of your monitoring and security tools. Niagara Networks can help you evaluate an ePacketron deduplication configuration and define a test using your traffic and tool requirements.

    Talk to a Visibility Expert