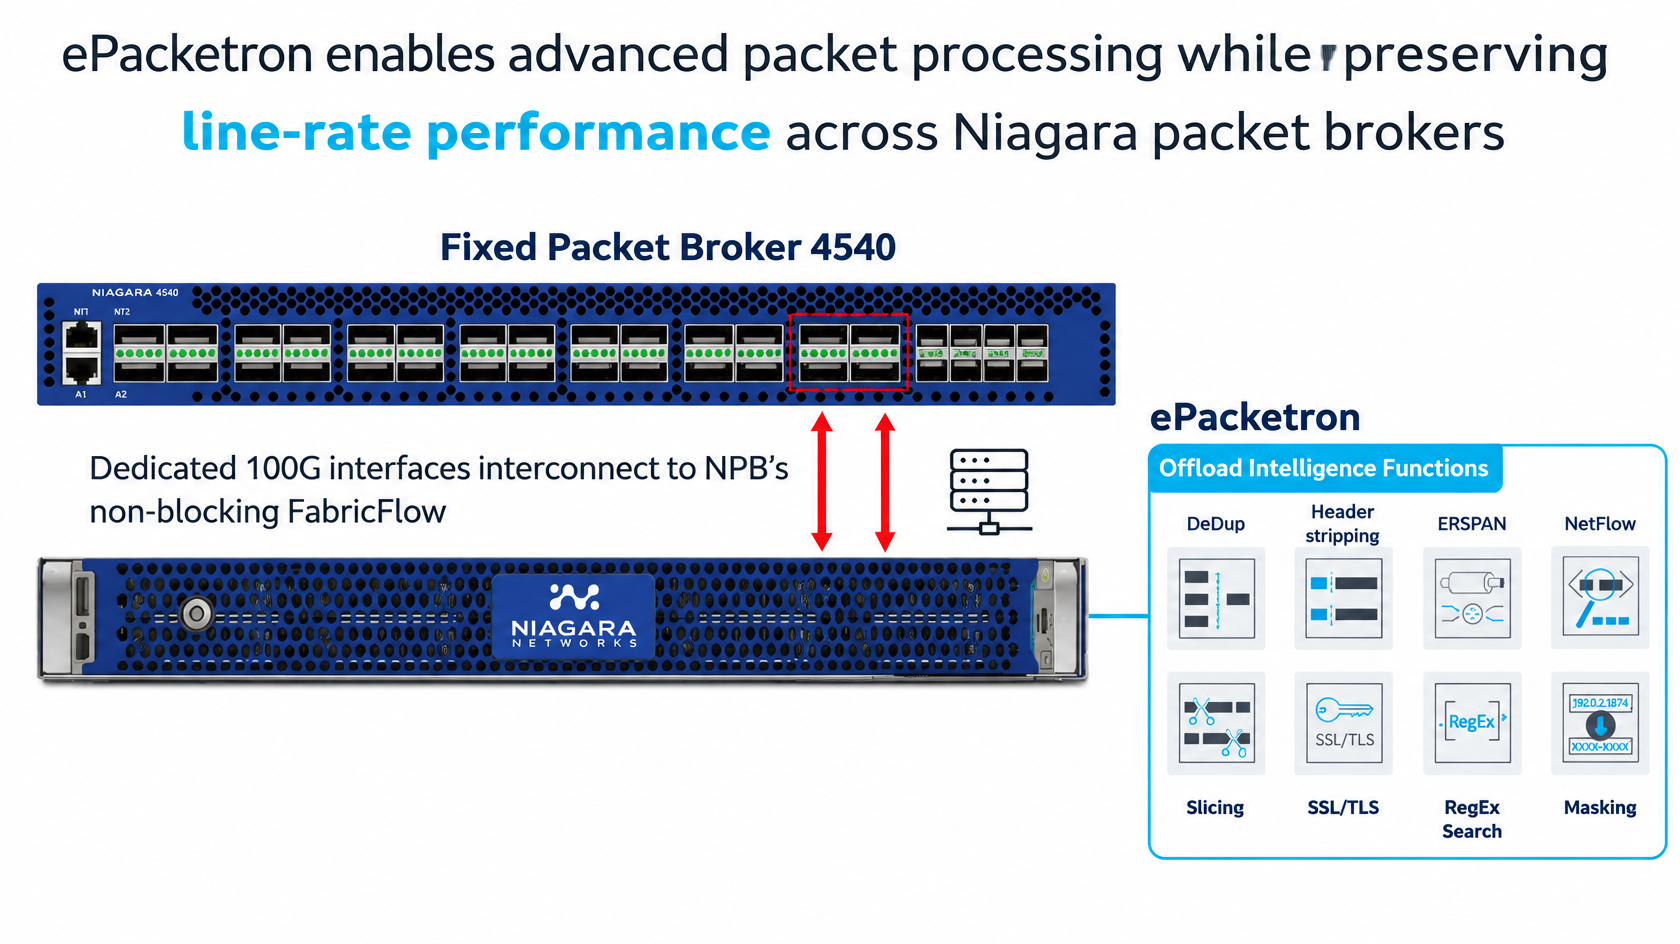
Niagara’s ePacketron-powered architecture transforms the visibility layer into a true Network Intelligence platform. Each application listed below is seamlessly deployable through the ePacketron Acceleration Solution, extending the traditional Packet Broker’s capabilities beyond traffic distribution into application-level and subscriber-aware visibility.
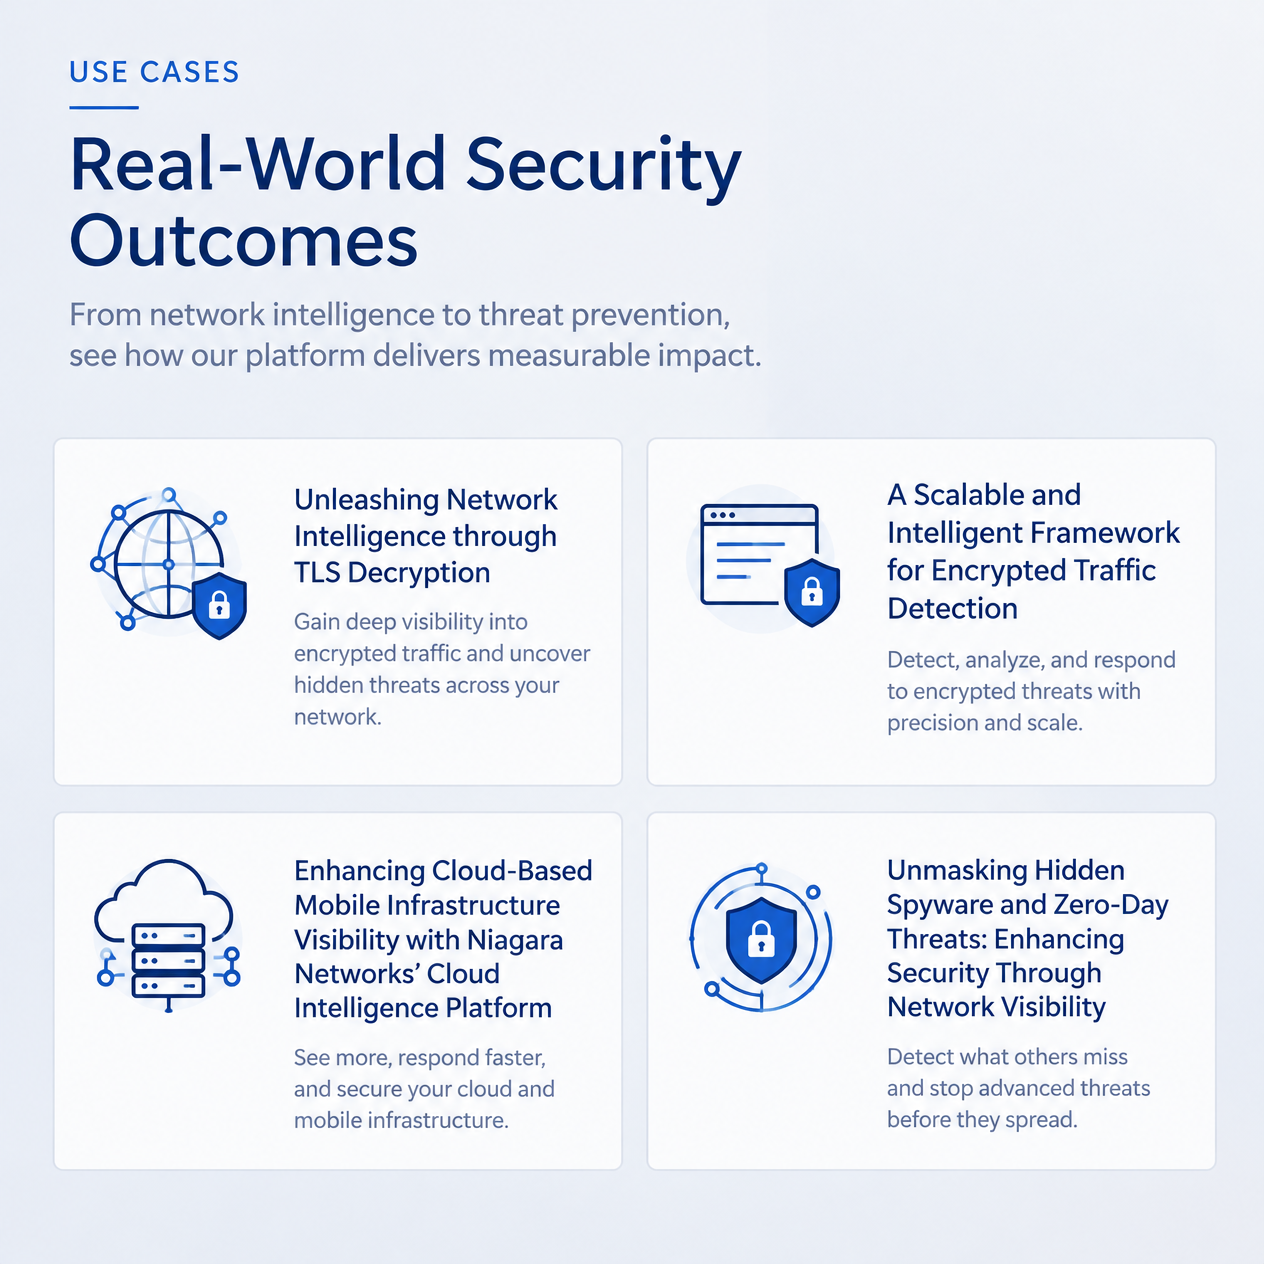
TLS Decryption & ECH-Aware Selective Inspection
Enables TLS 1.3 decryption for supported ECH connections. Apply configured actions - none, log, drop, or decrypt - and domain-category policies at the TLS handshake. Eligible traffic can be decrypted for inspection, while traffic excluded by policy remains encrypted. ECH handling requires supported clients that trust the enterprise CA.
Deduplication
Deduplication identifies and removes duplicate packets from being sent to a network appliance. While duplicate packets may occur on the network from backup and failovers deployment architectures, the more common occurrence is with the use of multiple SPAN ports across connected switches and routers that are feeding to a network appliance. When a network appliance handles duplicate packets, the duplicate packets consume the tools limited processing resources, resulting in significant performance degradation and may also affect the accuracy and results reported.
Packet Slicing
Packet Slicing reduces the volume of data to be forwarded for analysis and processing by a network appliance by reducing the packet length. This is especially useful for network applications that only require header analysis and or a defined set of bytes from each packet. Packet length is reduced based on user configurable rules.
Tunnel Support
Supports traffic handling across common tunneling protocols, including GRE, VXLAN, GTP, MPLS, ERSPAN, GENEVE, PPPoE, NVGRE, and FabricPath. Tunnel termination can deliver decapsulated traffic to downstream tools.
Header Stripping
Header Stripping is designed to facilitate and modify traffic in a manner that the intended network tool can process it and fulfill its intended purpose. Niagara’s application will strip the header from the traffic exposing the relevant packet for processing.
Data Masking
Data Masking enables the enterprise to forward and share data traffic across departments, while at the same time providing them with a tool to mask private and confidential user information that is contained in the data.
Regular Expression Filtering
Regex Patterns application, functions as an expansion for existing filtering and data masking capabilities, while adding additional new modes of operation. The user can define any pattern through a regular expression, or load a predefined expression. With this capability, the user can perform advanced packet filtering, advanced masking and advanced session filtering. With session filtering, once the pattern is detected in any packet, the entire session is identified and can be filtered. For every pattern match, the user can configure to filter or to exclude the match
NetFlow/IPFIX
With the increase in traffic capacity on the one hand and the need for greater processing granularity on the other, many network tools ingest traffic metadata rather than the raw traffic data packets themselves. There are well-standardized metadata frameworks as well as numerous specified fields and extensions for additional vendor-specific fields. Often, metadata reports are generated by the network element itself like a switch or a router. The disadvantage is that as metadata generation is not the primary objective of the switch or router, metadata performance generated by the switch or router may be degraded in times of congestion versus Niagara’s solution where such degradation does not take place. Furthermore, to address congestion, the switch or router utilizes traffic sampling, instead of taking into account every packet in the flow.
Mobile GTP Correlation
GTP Correlation encompases multiple applications associated with facilitating network tool connectivity in mobile environments. One of the primary challenges in mobile networks network tools, whether used for performance, monitoring, behavioral analysis, and or any other analysis that requires differentiating user traffic is that in mobile networks the user plane and control plane are decoupled. In order to correctly identify a specific user’s traffic we need to correlate it with the control/signaling plane. Other associated applications include optimized load balancing based on user traffic, IMSI filtering and more.
TCP Segment Reordering
Reorders TCP segments and suppresses retransmissions and duplicate acknowledgements in out-of-band monitoring feeds, providing downstream tools with an ordered traffic stream for analysis and session reconstruction.
Application Filtering
Identification of applications and layer 7 protocols often require deep packet inspection and analysis. Application filtering performs DPI and supports the identification of dozens of applications. Supported application list is updated on a regular basis.
Packet Reassembly
Reassembles fragmented IPv4 and IPv6 packets carrying TCP or UDP traffic, including fragmented packets inside tunnels, before filtering and delivery. This supports consistent filtering and downstream analysis in out-of-band deployments.
Flow Slicing
Forwards a user-defined number of initial packets from each flow, then discards subsequent packets from that flow. This lets monitoring tools inspect the traffic needed to identify and understand a session while reducing the packet volume they must process, helping conserve tool capacity and bandwidth.
Protocol Reporting
Protocol Reporting provides a comprehensive understanding of how network traffic is composed and consumed. By analyzing usage volume and breaking down flows by protocol, it delivers a clear picture of traffic distribution and utilization across the entire network. This visibility helps teams identify anomalies, validate performance baselines, and ensure that capacity and SLA targets are being met. With accurate insights into protocol behavior, organizations can optimize resource planning, troubleshoot issues faster, and maintain overall network health.
Packet Capture
Packet Capture empowers security and operations teams with granular access to the packets that matter most. By recording selected traffic for offline inspection, it enables detailed forensic analysis, retrospective investigation, and precise reconstruction of past events. This capability is essential for incident response, law-enforcement data requests, troubleshooting complex issues, and conducting post-breach analysis with confidence. Packet Capture ensures that no critical evidence is lost and that teams have the depth of visibility required to understand root causes and strengthen security posture.