close
close-x

Site Search

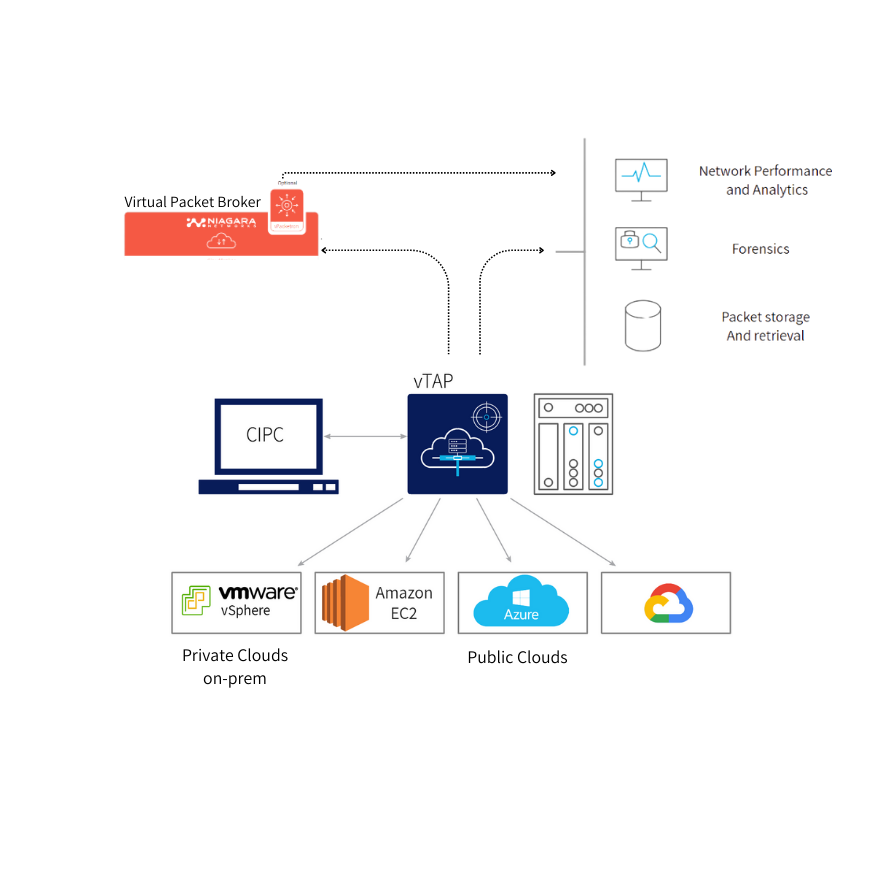
    vTAP Diagram

    Virtual TAPs for Cloud and Virtual Network Visibility


    A lightweight virtual TAP that captures, filters, and forwards East-West and inter-VM traffic across private clouds, public clouds, and hybrid environments.

    Physical TAPs are essential for physical links, but they cannot see traffic that stays inside a hypervisor, virtual switch, cloud VPC, VNet, or workload overlay. A virtual TAP closes that gap by capturing traffic close to the workload and forwarding it to security and monitoring tools.
    Niagara Cloud Intelligence TAP, or vTAP, extends packet visibility into private cloud, public cloud, and hybrid environments. It captures east-west, inter-VM, and cloud-native traffic, applies selective filtering, exports traffic through tunnels, and works with Cloud Intelligence Platform for centralized processing and tool delivery.

    With centralized management through the CIP Controller (CIPC) and seamless integration with Niagara’s physical TAPs, the virtual TAP ensures SOC, NOC, and cloud teams always gain full visibility into the right VM traffic - anywhere workloads run.

    vTAP - remove blind spots (1)

    A CLOUD-NATIVE VIRTUAL TAP THAT ELIMINATES BLIND SPOTS AND EXTENDS VISIBILITY ACROSS ANY CLOUD


    Intelligent
    • Full visibility into East-West, inter-VM, and mid-plane traffic
    • Selective multi-layer traffic filtering
      GRE-based export to any monitoring or security tool
    • Enhances troubleshooting, SLA compliance & forensics
    Adaptive
    • Deployed in private, public, and hybrid cloud environments (AWS, Azure, GCP)
    • Aligns with cloud-native networking models
    • Supports dynamic, autoscaling workloads where VMs frequently start, stop, or migrate
    • Works seamlessly with VMware vSphere and cloud VM platforms
    Unified
    • Works across AWS, Azure & GCP

    • Integrates with private & on-prem virtualization

    • Flexible policy profiles & unified
      control layer

    Scalable
    • High-throughput virtual architecture
    • Multi-region, multi-VPC visibility
    • Tool load optimization
    vTAP - complete visibility across hybrid cloud

    WHY CLOUD INTELLIGENCE TAP (vTAP) IS REQUIRED IN MODERN VIRTUALIZED & CLOUD ENVIRONMENTS?

    Traditional visibility tools were designed for physical networks, where traffic flows through predictable switching paths and can be tapped via SPAN ports or physical TAPs.
    Modern environments look nothing like that.

    Virtualized and cloud-native networks introduce blind spots that traditional TAPs simply cannot reach:

    • East–West and inter-VM traffic stays inside the hypervisor - never hitting a physical interface
    • VM-to-VM communication is switched internally through vSwitches
    • VMs and containers start, stop, and migrate dynamically
    • Cloud providers encapsulate traffic using VXLAN, GENEVE, and GRE
    • Native cloud routing and micro-segmentation isolate workloads
    • Autoscaling and multi-zone designs constantly change traffic paths
    • Cloud providers often restrict or eliminate access to raw packet data


    This means physical TAPs, SPAN ports, and legacy packet brokers cannot see where the traffic actually flows. Virtual TAP solves this core challenge by bringing lightweight, native visibility directly into virtual and cloud workloads.


    How Niagara vTAP Works with CIP

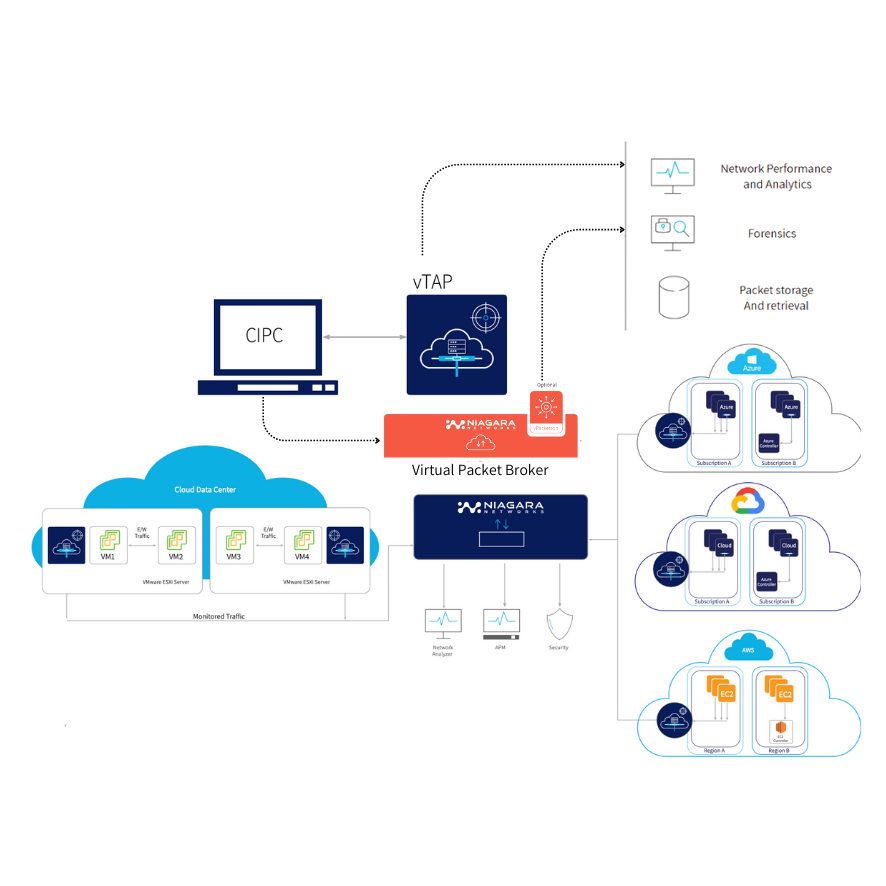
    • vTAP captures selected traffic close to virtual or cloud workloads.
    • Traffic is filtered before export to reduce tool load and cloud bandwidth consumption.
    • Traffic can be tunneled to Cloud Intelligence Platform or approved monitoring and security tools.
    • CIP aggregates, filters, deduplicates, slices, enriches, and distributes cloud traffic.
    • Physical TAPs and packet brokers can be combined with vTAP/CIP for hybrid visibility.
    Built for Virtual & Cloud-Native Blind Spots

    Virtual TAP captures East–West, inter-VM, and mid-plane traffic that never leaves the server or hypervisor.
    It eliminates blind spots created by virtualization layers and cloud networking models - delivering 100% visibility into VM traffic across private, public & hybrid clouds.

    Close to Workloads

    vTAP runs inside the virtualized environment and collects the right traffic at the source, before it is encapsulated or distributed across zones.
    VMs can start, stop, and migrate - vTAP follows the workload, ensuring visibility continuity across hypervisors, regions & cloud platforms.

    Traffic Reduction Before Sending to SOC/NOC Tools

    vTAP reduces overhead and tool load by applying selective, multi-layer filtering:

    • Removes unnecessary packets

    • Reduces bandwidth consumption

    • Sends only relevant monitored flows to collectors

    Traffic is exported efficiently using GRE tunneling, enabling integration with any monitoring, security, or analytics tool.

    Unified, Scalable Visibility Across Hybrid Clouds

    Managed centrally by the CIP Controller, vTAP provides a unified operational model across:

    • VMware environments

    • AWS, Azure, and GCP workloads

    • On-prem data centers

    • Multi-cloud and hybrid-cloud deployments

    Bulk deployment, minimal overhead, and seamless integration with Niagara physical TAPs ensure visibility everywhere - at any scale.

    CAPTURE, FILTER, AND FORWARD VIRTUAL TRAFFIC ACROSS CLOUD & VIRTUALIZED ENVIRONMENTS

    Cloud Intelligence TAP (CIT) delivers complete visibility into East-West, inter-VM, and cloud-native traffic that traditional TAPs cannot access - ensuring SOC, NOC, and cloud teams receive the right packet data for monitoring, security, and analytics

    Cloud-Native VM Visibility

    • 100% visibility into VM, East-West, inter-VM, and mid-plane traffic

    • Deploys in AWS, Azure, GCP, and private virtualized environments

    • Supports hybrid and multi-cloud architectures

    • Continuously tracks VMs as they start, stop, or migrate across hosts and clouds

    Selective Traffic Filtering & Tunnel Export

    • Multi-layer, selective filtering reduces bandwidth and tool load
    • GRE tunneling support for exporting traffic to any monitoring or security platform
    • Forward traffic to multiple collectors in cloud or on-prem environments

    Smart Integration with Cloud & Virtual Networks

    • Native compatibility with VMware ESXi, vSS & vDS
    • Supports IPv6 TAP across AWS, Azure, and GCP
    • Aligns with cloud-native networking models (VXLAN, GRE)
    • Complements Niagara physical TAPs for full hybrid visibility

    Centralized Management & Automation

    • Unified administration through the CIP Controller for all vTAPs
    • Manage traffic policies, deployment, and orchestration from one interface
    • Enable consistent visibility architectures across private, public, and hybrid clouds

    Lightweight, Scalable Virtual Architecture

    • Minimal hypervisor overhead with efficient VM resource usage
    • One-touch installation enables fast, bulk deployment
    • Scales elastically across multi-zone and multi-region cloud environments
    • Supports high-density deployments with large cloud footprints
    vTAP use cases (1)

    Use Cases

    Cloud Intelligence virtual TAP enables consistent visibility across private cloud, public cloud, and on-prem data centers, ensuring SOC/NOC teams receive the right packet data regardless of where workloads move.

    CIT captures East-West, inter-VM, and mid-plane traffic inside VMware, AWS, Azure, and GCP environments - eliminating blind spots that physical TAPs cannot reach.

    Spyware and zero-day attacks are designed to be invisible, but with strong network visibility, they increase the chances of early detection and effective response. Visibility is a foundational layer, but pairing it with effective analysis and rapid response is essential to neutralize threats. By strategically using modern security tools and maintaining comprehensive monitoring, organizations can reduce their vulnerability and defend against today’s most sophisticated cyber threats.

    Cloud Intelligence TAP - Virtual TAP – Frequently Asked Questions (FAQ)

    A vTAP is a virtual traffic access point that captures traffic in cloud or virtual environments where physical TAPs cannot see the packets.

    A physical TAP captures traffic from a physical link. A vTAP captures traffic inside virtualized or cloud environments, closer to workloads and virtual switches.

    Physical TAPs cannot see internal hypervisor traffic because East-West and inter-VM packets never leave the virtual switch. CIT captures this hidden traffic, eliminating blind spots inside VMware, AWS, Azure, and GCP workloads.

    CIT supports VMware ESXi, Amazon EC2, Microsoft Azure, and Google Cloud Platform, including IPv6 TAP capabilities. It operates seamlessly across private, public, and hybrid cloud environments.

    CIT uses GRE tunneling to send filtered traffic to any security, analytics, or monitoring tool - whether deployed in the cloud or on-prem. It also supports forwarding to multiple collectors at the same time.

    No. CIT is designed for minimal resource usage, with ultra-light VMs (1–2 vCPUs and low memory requirements), ensuring negligible impact on production workloads.

    Management is centralized through the Cloud Intelligence Platform Controller (CIPC), which provides unified orchestration for virtual TAPs and virtual packet brokers across cloud and on-prem environments.

    CIT is the virtual TAP component that captures traffic, while CIP provides the centralized management and virtual packet broker capabilities. CIT collects the packets; CIP orchestrates and distributes them.

    Yes. CIT supports bulk deployments, integrates with dynamic, autoscaling cloud workloads, and maintains persistent visibility even as VMs start, stop, or migrate across regions or hypervisors.

    CIT supports selective traffic filtering. This reduces bandwidth consumption and optimizes downstream tool load by forwarding only relevant packet flows.

    Yes. CIT complements Niagara’s physical visibility layer, enabling end-to-end visibility across hybrid environments where both physical and virtual components coexist.

    Licensing is based on the number of installed vTAP agents, available in subscription bundles ranging from 10 to 1000 agents, including Docker-based agent packs for cloud workloads.

    Cloud Intelligence TAP (CIT) is Niagara Networks’ virtual TAP solution. “Virtual TAP” is the industry term, while “CIT” is the product name. Both refer to the same software technology that captures East-West and inter-VM traffic inside virtualized and cloud environments.

    Yes. CIT is a vTAP (virtual TAP) - a software-based TAP designed to monitor internal traffic flows within hypervisors and cloud platforms such as VMware, AWS, Azure, and GCP.

    We use the name Cloud Intelligence TAP to emphasize that the solution delivers more than basic packet mirroring. CIT provides cloud-aware visibility, selective filtering, centralized orchestration, and hybrid-cloud readiness - all capabilities beyond a traditional vTAP.

    Capture the virtual traffic your physical TAPs cannot see. 

    Niagara Networks vTAP helps SOC, NOC, and cloud teams capture east-west and inter-VM traffic, then route optimized streams through CIP and Cloud Packet Broker workflows.


    Fill out the form and our team will connect with you to explore how our solution can strengthen your network visibility strategy.


    Designed, Engineered & Manufactured in the USA

    From design to production, our solutions are built to the highest standards of quality, security, and performance, trusted by organizations worldwide and deployed in some of the world’s largest mission-critical networks.

    Connect with a Visibility Expert